Prolific Cybercrime Marketplace WT1SHOP Shut Down in Law Enforcement Operation
Read also: Albania cuts diplomatic ties with Iran over a cyberattack, a new Apple zero-day is being sold on the dark web, and more.


Read also: Albania cuts diplomatic ties with Iran over a cyberattack, a new Apple zero-day is being sold on the dark web, and more.
The August 4th compromise of Twilio via a targeted smishing attack has been a topic of wide concern and discussion on social media. My first thoughts on hearing of the attack were to virtually “pat myself down” with regard to exposure risk. Kind of like that feeling when you’re not sure if your car keys or wallet are in your pocket a few blocks after walking away from your parking space. Is my company affected by the breach? Did we receive a notification email from them?
In August 2022, password management company LastPass fell victim to a cyberattack, in which hackers breached its systems and stole its source code. LastPass’s success is built around offering secure, trustworthy software, so a hack like this could be seen as a knock against the company — but it also impacts wider public trust in password management software.
There is always the risk that sensitive data will be exposed during mergers and acquisitions. Throughout the M&A process, you’re adding new ways for hackers to enter your systems, enabling them to access sensitive customer information. This is because the merging of companies usually results in an increase in the attack surface, therefore, increasing the number of unknown security risks the acquiring company is unaware of. The numbers don’t lie.
Almost a year ago, Gartner predicted that API attacks would be the most frequent enterprise attack vector in 2022. Strengthening API security is more critical today than ever and must be at the core of cybersecurity strategy to prevent API exploitation. To make matters worse, the lack of API visibility weakens core security principles. More organizations don’t have an accurate inventory of APIs, and it is not surprising for 30% of APIs to be unknown.
In the introductory post of this series, we reviewed what an Active Directory (AD) service account is, explained why these privileged accounts are a serious security risk, and promised to detail 4 types of attacks on service accounts in future posts. This post explores the first of those attacks: LDAP reconnaissance, which attackers can use to discover service accounts in an IT environment while avoiding detection.
In the first post of these series we showed how an adversary can discover Active Directory service accounts with PowerShell, and the second post demonstrated how to crack their passwords using the Kerberoasting technique. Now let’s see how an attacker can exploit a compromised service account using Kerberos Silver Tickets to forge TGS tickets.
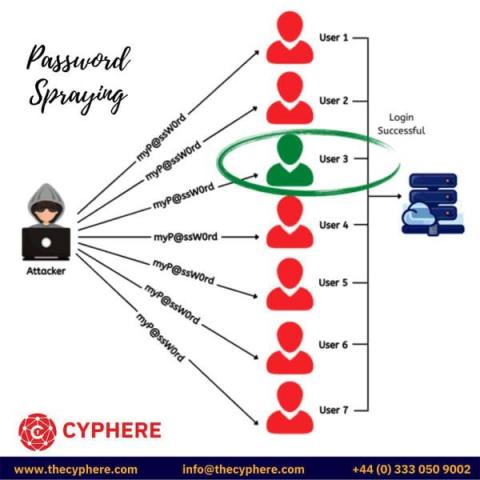
Passwords are an easy way to implement an authentication mechanism in which the user is asked to enter a string of characters (that he had chosen) to log in to his accounts. We will cover brute force attacks, types and examples in this blog article.
Crypto miners are determined in their objective of mining in other people's resources. Proof of this is one of the latest samples identified with AT&T Alien Labs, with at least 100 different loaders and at least 4 different stages to ensure their miner and backdoor run smoothly in the infected systems.