Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Best AI Governance Platforms for Mid-Market Companies

Enterprise AI governance guidance assumes a review board that meets monthly, an independent validation function, an impact assessment per system and somebody whose job title contains the words AI and compliance. A company of three hundred people has none of those and is governed by the same regulations. ‍ The difference runs deeper than budget. Enterprise programs are assessment-led, which scales with headcount because every system needs an assessor.

Governing at the speed of AI: What IT leaders need to know

AI is reshaping the IT leadership role faster than any shift in the last decade. As AI makes it dramatically easier to build software (agents, apps, automations, and more), the volume of software entering the enterprise is far beyond what IT teams have had to govern before. That shift demands new ways of thinking about enterprise control: how security, access, and oversight evolve to keep pace with software that's built faster and by far more people than ever before. The leaders who treat this as an operating shift, not just a technical one, are the ones expanding their influence.

AI Governance Where the Regulator Also Runs the Market

AI governance evidence is usually prepared for a neutral reader. A regulator with no stake in the market, an auditor with no competing product, an examiner who gains nothing from what the documentation contains. ‍ In securities and derivatives markets that assumption does not hold. Exchanges and clearing organizations register as self-regulatory organizations, and most of them operate the market while regulating its participants. The reader of your evidence is also an operator. ‍

What Is Identity Governance and Administration (IGA)? A Complete Guide

Disconnected identity systems create the access risk, audit friction, and IT overhead that identity governance and administration (IGA) is built to close. The 2026 Verizon Data Breach Investigations Report found credential abuse in 39% of breaches. IGA combines policy, certification, and compliance evidence with automated provisioning, deprovisioning, and access requests to keep access aligned with business needs and reduce that risk.

AI Governance for Content Nobody Has Released Yet

Confidential data is usually something to protect indefinitely. Customer records, financial results, contract terms and personal information all need the same treatment next year as this year, so controls are judged on how well they hold over time. ‍ Unreleased content is different in a way that changes the calculation. Its commercial value depends entirely on not existing publicly yet, and on release day that requirement disappears completely.
Featured Post

Why Data Governance Has Become a Critical Defence Against Ransomware in Healthcare

Ransomware and ransomware-style attacks can have a catastrophic impact within healthcare, where disruption directly impacts safety and continuity. Today's ransomware groups increasingly operate as sophisticated criminal enterprises, sharing tools, infrastructure, and expertise through ransomware-as-a-service (RaaS) models. This lowers the barrier to entry for cybercriminals while allowing experienced threat actors to focus their efforts on identifying and exploiting high-value targets.

AI Governance When the AI Is Inside the Network

Most AI governance guidance assumes the AI sits beside the business. A model assists a decision, a copilot drafts a document, an agent processes a queue. Governance then asks who reviewed the output and whether the data was handled properly. ‍ In a telecom network the AI is inside the product.

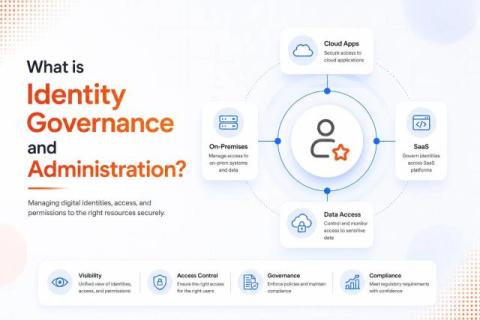
What is Identity Governance and Administration (IGA)?

Enterprises today manage thousands of identities across employees, contractors, applications, APIs, and machine-driven systems. In most environments, identities have become the primary security boundary, yet access remains fragmented, overprovisioned, and difficult to track. According to IBM's X-Force Threat Intelligence Index, identity-based attacks now account for nearly one-third of all intrusions, highlighting how identity has become one of the most targeted layers in modern cybersecurity.

Best Shadow AI Governance Tools for Enterprises: Buyer's Shortlist

Security teams already know employees use generative AI. The harder problem is buying the right platform before unsanctioned apps move sensitive data outside your visibility and control. UpGuard research found 81% of employees and 88% of security leaders use unapproved AI tools, and 45% of workers find a workaround when their employer blocks an app. That last number should shape your buying criteria more than the first two. Demand doesn't disappear when you block it. It moves somewhere you can't see.