Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The first 72 hours of a ransomware attack: Why restored isn't recovered

You start the day with reports that your employees cannot access critical systems. A ransom note soon explains why: attackers have encrypted them and demand $2 million in bitcoin for a decryption key. Your team contains the attack and confirms that the backups are safe, yet this is only the beginning. Restoring your servers can take weeks, but recovering the business can take much longer.
Zero-Day Attack Prevention: Catching Unknown Vulnerabilities Before Threat Actors Do

On September 1, 2026, OpenAI announced that its Astra model had reached the Critical tier for cyber capability under the company’s Preparedness Framework, a first for its systems. While working through an internal benchmark of 20 recently disclosed vulnerabilities in Google’s V8 engine, the model found two zero-days that no one had asked it to look for and used them in a working exploit chain. OpenAI is disclosing both flaws and restricting the capability to vetted testers.

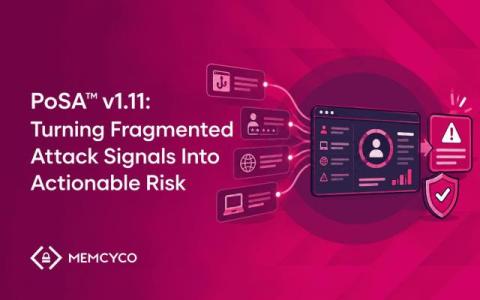
PoSA v1.11: Turning Fragmented Attack Signals Into Actionable Risk

With PoSA v1.11, we focused on a practical problem: detecting more attack activity does not necessarily help fraud and security teams make better decisions. PoSA already identifies activity across digital impersonation, credential theft, attacker devices and account access. The challenge is making the connections between that activity easier to understand, identifying which users and devices require attention, and making that intelligence available to the systems and teams responsible for responding.

The New Rules of Patching: When a Fix Becomes a Blueprint for Attackers

TL;DR: Frontier AI has collapsed the vulnerability exploit window from weeks to mere hours. Attackers now use advanced AI models to reverse-engineer published fixes and generate working exploits faster than human security teams can deploy updates. In the AI era, publishing a patch creates a blueprint for attackers. Surviving this threat requires vendors to tier sensitive disclosures and customers to treat patch application speed as a critical security metric.

Phone Numbers as an Attack Surface: What SIM Swap and Data Leaks Actually Expose

The majority of security teams' work time is devoted to passive mitigation, password rotation, enabling multifactor authentication, or making authentication more complex and giving much more attention to the phone number in recovery than to other factors. Not a communication channel, but rather an identifier, as said, it's used in many aspects of tools, banking, and also e-mail, and when all thieves discover the methods of using it, that's when trouble arrives.

Kiteworks recommends server shutdown pending possible attack

On September 25, 2026, reports emerged that Kiteworks (formerly Acellion) emailed customers that law enforcement alerted them about an “imminent” cyberattack on Kiteworks systems, possibly caused by exploitation of a zero-day vulnerability. Kiteworks reportedly advised customers to shut down servers between 02:00 and 08:00 UTC on September 26, if not sooner, as a “precautionary” measure.

The water system attacks were simple. Securing OT isn't.

Recent cyberattacks against U.S. water and wastewater systems have put some familiar operational technology (OT) security problems back in the headlines. Federal agencies have warned about malicious actors targeting internet-facing programmable logic controllers (PLCs), changing device configurations, and disrupting operations at utilities across multiple states.

DMARC Explained: How to Stop Attackers From Impersonating Your Domain

Email is still the most common way attacks begin. Phishing, business email compromise, and brand impersonation all rely on one simple weakness: by default, anyone can send an email that claims to come from your domain. The protocol that email runs on was never built to verify who a sender really is, so a criminal can forge the "From" address to look exactly like it came from your company, and the receiving mail server has no built-in way to know the difference. That is the gap attackers exploit, and it is the gap DMARC was designed to close.

Protecting Assets from Cyber-Physical Attacks

Our digital and physical worlds are now closely linked. This connection brings incredible efficiency, but it also creates new vulnerabilities. When digital systems control physical infrastructure, a security failure can have real, tangible consequences. Protecting your assets today means having a strategy that tackles threats in both these areas at the same time.