Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

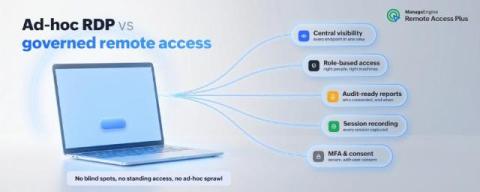
Why unmanaged RDP is risky at enterprise scale (and how to regain control)

Remote Desktop Protocol (RDP) is the path of least resistance for gaining access to another Windows machine. It is built into the OS, it is free, and almost every admin and help desk technician already knows how to fire up mstsc.exe and type in a hostname-as simple as that. That convenience is exactly why RDP is everywhere inside corporate networks.

New Phishing Kit Gives Threat Actors Live View Into Attacks

A new phishing platform called “JWR” gives attackers real-time control over social engineering attacks, according to researchers at Cisco Talos. The kit livestreams the phishing page to the attacker as the victim is entering information, allowing the attacker to steer the victim’s experience and maximize the damage.

Voice Phishing Attacks Target Hedge Fund Employees

Google’s Threat Intelligence Group (GTIG) is tracking a voice phishing (vishing) campaign that’s targeting hedge funds and financial firms. The researchers attribute the attacks to “UNC6671,” an extortion group formerly known as “BlackFile.” The attackers pose as IT staff informing employees of urgent, mandatory migrations.

What is DLL hijacking, and why your new AI plugin might be the easiest way in

DLL hijacking is a decades-old Windows vulnerability class (Mitre Att@ck T1574) getting new life from AI plugins bolted onto legacy desktop apps. Attackers plant a malicious DLL where a vulnerable app will load it instead of the real one, inheriting that app's privileges. To detect it, watch for DLLs loaded by name from writable folders. To prevent it, you have to fix the app's load-order logic or blocking untrusted DLLs at the endpoint.

Attackers Use Vishing Attacks to Distribute New Android Malware

Attackers are distributing a new Android malware called “WindRelay” via phone-based social engineering attacks, according to researchers at Group-IB. The attackers call the victims, impersonating bank employees and instruct them to install a malicious app. In one instance observed by Group-IB, the scammers carried out the entire attack in just thirteen minutes.

Steps to Recover from Ransomware Attacks Efficiently

A ransomware attack can stop business operations in a very short time. Files may become locked, systems may go offline, and employees may lose access to important tools. In some cases, attackers may also steal data before blocking access to it. Recovering from ransomware takes more than simply restarting computers. Businesses need a clear plan for containment, investigation, data recovery, system repair, and future protection. A rushed response may make the damage worse or allow attackers to return.
Featured Post

How Geopolitics is Driving Modern Cybercrime

Ransomware attacks no longer rely on traditional encryption methods. With today's advanced technology, threat actors are developing 'encryption-less extortion', focusing solely on data exfiltration and the threat of leaking or selling stolen sensitive information. Often used as part of double and even triple extortion strategies, ransomware has now evolved into a fragmented, competitive, and increasingly strategic threat landscape that employs divergent attack strategies, laser-focused on high-value targets.

Donation Forms Attract Card Testing Attacks

A charity notices something odd in its payment dashboard. Hundreds of one dollar donations attempted overnight. Almost all declined. A handful approved. Nobody donated anything. The organization was being used as a validation service. Donation forms have become a preferred target for card testing, and the reasons are structural rather than accidental. Here is how the attack works, why nonprofit payment pages are disproportionately attractive, and what actually stops it.

Living Off the Land Attacks: Detection and Response Guide

The most popular advice about living off the land attacks is also the least useful when it stands alone: hunt for suspicious PowerShell, block LOLBins, and alert whenever a signed Microsoft binary behaves unexpectedly. Those controls have value, but they don't solve the operational problem. PowerShell, WMI, certutil.exe, and bitsadmin.exe are legitimate administrative utilities, and attackers abuse them precisely because security teams can't remove them without disrupting normal work.