Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PCI Compliance Logging: Complete Guide to Requirement 10

Of the 12 Payment Card Industry Data Security Standard (PCI DSS) requirements, Requirement 10 is one your platform team can engineer directly. Under the PCI DSS v4.0.1 standard, automated log review has been a tested requirement since March 31, 2025. Your assessor will test the mechanism that performs the review. This PCI compliance logging guide covers each 10.x sub-requirement, maps the seven event classes to log sources, and lays out a nine-step program you can hand to your assessor.
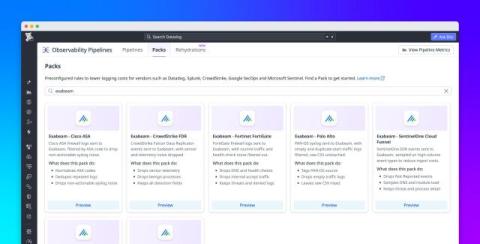
Process and route critical security logs to Exabeam with Observability Pipelines

Enterprise security teams use Exabeam as a security information and event management (SIEM) platform with user and entity behavior analytics (UEBA) to detect insider threats, lateral movement, privilege escalation, credential compromise, and data exfiltration.

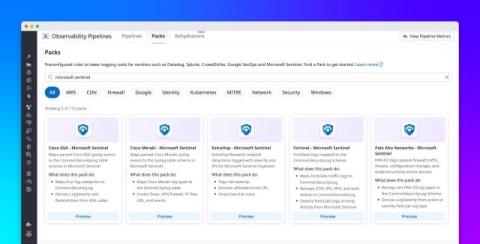
Transform and route security logs to Microsoft Sentinel tables using Observability Pipelines

Microsoft Sentinel is Microsoft’s cloud-native SIEM for detecting, investigating, and responding to threats across your environment. To query security data and run analytics rules, Sentinel expects telemetry data in specific table schemas. But firewall, VPN, and network detection logs arrive in vendor-specific formats, making source-specific mappings difficult to maintain as environments grow.

What Are Syslogs and How They Power Modern SIEM Detection

You're in the middle of a noisy SOC shift, and a firewall alert lands late. The device was supposed to send logs over syslog, but the path was UDP-based and the network dropped the messages under stress. By the time an auditor asks for proof, the team has an investigation, a gap in the timeline, and no clean evidence trail to show what happened.

Meeting HIPAA Log Retention Requirements in 2026

You're usually not thinking about retention when the week starts. You're thinking about alert noise, an audit request from compliance, and a storage bill that keeps climbing because logs are piling up in your SIEM, EDR, or XDR stack. Then someone asks a simple question, and the answer isn't simple at all. Which logs must be kept, for how long, and where do you stop using hot storage and start preserving evidence for HIPAA?

Windows Event Log Analysis: A Practical Guide

If you're staring at a flood of Windows telemetry at 2 AM, the problem usually isn't that the logs are useless. The problem is that nobody turned them into a workflow. Raw Security, System, PowerShell, and Defender events can tell you exactly what happened, but only if collection, parsing, triage, and reporting are handled like part of the same control, not four separate chores.

Best Log Management Tools for 2026 Security

Enterprises are already spending an average of nearly US$2.5 million annually on logging solutions, and those tools consume 45% of observability budgets while teams juggle an average of seven different tools to manage logs and telemetry (enterprise logging spend and tool sprawl). That's the reason log management tools have moved from back-office utilities into security architecture decisions.

Find and stop vulnerable code at runtime - Secure App in Splunk Observability Cloud

Secure App brings runtime application security into Splunk Observability Cloud using the same OpenTelemetry instrumentation as your APM traces to surface the vulnerabilities actually running in production, prioritize them by real-world exploit risk, and catch live attacks. TOC.

Top 10 Log Aggregation Tools for 2026: SIEM & Compliance

You're staring at a growing pile of endpoint, cloud, firewall, and identity logs, and the question isn't whether the data is useful, it's whether you can turn it into evidence, detections, and a defensible audit trail. In regulated environments, HIPAA, PCI, and CMMC don't care that your team is busy, they care that logs are collected consistently, normalized correctly, retained properly, and searchable when an incident or audit hits.