Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CREST Vulnerability Assessments: The Total Guide

Established in 2006, CREST, or Council of Registered Ethical Security Testers is a non-profit membership body. It aims to vet both cybersecurity-providing organizations and security-testing individuals on their capacities, processes, and the standard of services provided. One of the accreditations provided by CREST is vulnerability assessments provided by companies. They are then differentiated as CREST vulnerability assessments.
Vulnerability Assessment vs. Penetration Test: A Case of Mistaken Identities

If you’ve been in the realm of penetration (“pen”) testing in any capacity for any length of time, you’ve probably experienced the conversations around inconsistent pen testing results across teams or vendors. This isn’t anything new in the pen testing world. The conversations probably ranged from friendly internal team banter to more serious discussions with external vendors on pen testing program success metrics. Is this a case of mistaken identity?

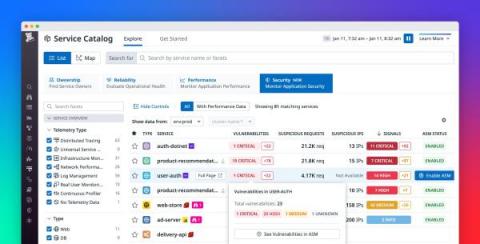
Gain visibility into risks, vulnerabilities, and attacks with APM Security View

As your business grows and your services scale in number and complexity, it’s difficult to maintain a rapid pace of innovation while keeping your applications secure. It’s particularly challenging to respond to attacks, as DevOps and security teams need to collaborate to understand each attack’s root cause and remediate the vulnerabilities that enabled it.

What is vulnerability scanning?

Vulnerability scanning is the action of conducting an automated review of your system to look for potential risks and vulnerabilities. For budding information security professionals (or even those who have worked in the field for years), there is always something new to learn. Not only is it a highly intricate and advanced field but, on a daily basis, there is a cat-and-mouse game happening between security engineers and hackers.

Veracode SCA Scan for VS Code Plugin

Introducing the Veracode SCA Scan for VS Code Plugin Developers can now: · Run an SCA Scan with Veracode· Identify vulnerabilities and license risks in open-source dependencies· Prioritize and rapidly fix any issues· Access the Veracode database, remediation guidance, and more All from within VS Code! Easily download the extension from the VS Code Marketplace.

CVE-2022-47966: Researchers to Release PoC Exploit for Critical Vulnerability Affecting ManageEngine Products

Later this week, Horizon3 researchers plan to release a Proof of Concept (PoC) exploit for CVE-2022-47966, a critical unauthenticated, remote code execution vulnerability in multiple ManageEngine products. Note: CVE-2022-47966 is dependent on the specific ManageEngine product. Some products are vulnerable if SAML single-sign-on is enabled OR has ever been enabled, while others require SAML single-sign-on to be currently enabled.