In the Clouds: Risk Management with Molly Mullinger and Abheer Bipin
Molly Mullinger, Director of Product Solutions, and Abheer Bipin, Senior Product Manager, team up to tackle some hot topics regarding risk management.


With the establishment of the EU General Data Protection Regulation (GDPR) and the expanding international landscape of data protection laws, organizations today face complex requirements and heightened scrutiny when it comes to data privacy. In addition, public awareness of data exploitation and digital surveillance is growing, and individuals are more concerned than ever about data privacy.
In today’s ever-changing business landscape, managing risk is crucial for the success and longevity of any organization. From financial risks to operational risks and cyber threats, businesses face a range of challenges that require a robust and secure risk strategy. With the complexities of modern business, risk management can no longer be put on the back burner, and companies will need to keep up with the latest practices and solutions to stay afloat.
The cybersecurity landscape is becoming increasingly complex and challenging for businesses of all sizes. As an MSP, you're well aware of the growing demand for comprehensive security and compliance solutions. With the right tools and strategies in place, you can help your clients navigate this complex landscape while unlocking new revenue streams for your business.
When you start pursuing compliance for a particular security standard, you do it with a specific goal in mind. Maybe you’re pursuing compliance because it’s a legal requirement in your industry or because a prospective customer requires it. But what happens after you achieve that initial SOC 2 or ISO 27001? It’s easy to get caught up in checking the boxes and lose sight of the why behind your security and compliance work.
Our team has been hard at work creating updates and new features just for you, see what we’ve been up to over the last month.
The SOC 2 framework helps you identify potential risks to your business and mitigate them with approved controls. To pass a SOC 2 audit, you must first define your audit objectives, determine your audit scope, and undergo a number of preparation steps and assessments. While these steps can be time-consuming, expensive, and arduous, achieving SOC 2 compliance can have huge business benefits for organizations, from improved compliance risk management to more sales opportunities.
Answering a GRC (Governance, Risk, and Compliance) vendor assessment is an important step for companies that want to demonstrate their commitment to compliance and risk management to potential customers. In this piece, we’ll cover how you can best respond to a prospect’s vendor assessment so you both can seal the deal. By following these best practices, you’ll be able to provide a comprehensive and accurate response to the assessment and establish a positive working relationship.
Today I’m excited to share the latest milestone in our growing partner ecosystem: Vanta has joined the Amazon Web Services (AWS) Independent Software Vendor (ISV) Accelerate Program. The AWS ISV Accelerate Program is a co-sell program for AWS Partners who provide software solutions that run on or integrate with AWS. Vanta’s acceptance into the program enables us to work in close collaboration with the AWS sales team to meet customer needs and provide better outcomes.
When you buy a new house, you shouldn’t have to worry that everyone in the city can unlock your front door with a universal key before you change the lock. You also shouldn’t have to walk around the house with a screwdriver and tighten the window locks and back door so that intruders can’t pry them open.
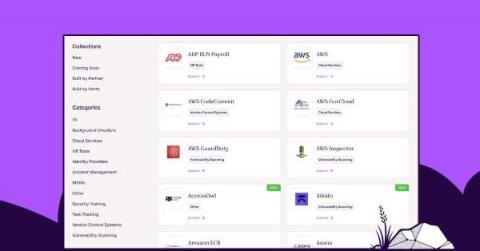
We’re thrilled to announce that we’ve delivered more than 50 new system integrations over the past quarter, taking us to a total of 110 integrations. This is far ahead of any other automated compliance solution in the market, reflecting our innovation velocity and long-term commitment to ensuring customer value and success with Vanta.
Anti-money laundering (AML) compliance in the mobile money industry has become increasingly important in 2023. With the rise of mobile money transactions, regulatory bodies are ramping up efforts to combat money laundering and terrorist financing. In this infographic, we explore the technology involved in AML screening, the importance of AML compliance in the industry, and best practices for financial institutions.
Following our recent acquisition of Trustpage, we are excited to announce Questionnaire Automation, a solution designed to help organizations in quickly responding to security questionnaires and effectively communicating security and compliance to customers and prospects. This solution utilizes the fastest and most accurate automation technology to provide security questionnaire responses.
SOC 2 is a compliance standard for service organizations, developed by the American Institute of CPAs (AICPA), which specifies how organizations should manage customer data. SOC 2 is based on five overarching Trust Services Criteria (TSC): security, availability, processing integrity, confidentiality, and privacy. Specifically, the security criteria are broken down into nine sections called common criteria (CC).
In November 2022, the Criminal Justice Information Services (CJIS) division of the FBI updated its cybersecurity policy, impacting state agencies, police departments, and other organizations that handle Criminal Justice Information (CJI). The updated policy poses challenges for organizations, especially smaller ones, to maintain compliance due to limited resources, lack of expertise and the policy’s complexity.
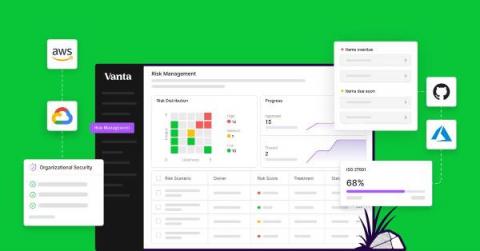
A risk register is a tool used to manage potential problems or risks within an organization. It helps to identify and prioritize risks, their likelihood of occurrence, and provides ways to mitigate them. Risk registers allow you to play offense and defense – you’re proactively planning for potential challenges and minimizing their impact on your project’s success in the event that the roadmap does veer off course.
At Vanta, we’ve been on a mission to secure the internet and protect consumer data from day one. We got our start building an automated compliance tool to help companies achieve SOC 2 compliance quickly and painlessly.
This past month at Vanta we launched a new brand, 32 new integrations, support for multiple & distinct identity providers (IdPs) and much more to improve the Vanta experience:
As the world has evolved in significant ways over the past several decades, so have the threats that businesses face daily evolved. In particular, cybercrime has grown into a nefarious force that harms businesses and causes irreparable damage. From holding information ransom to stealing private financial information, there is no limit to the damage that cybercriminals can inflict upon your operations.
Data from the International Organization for Standardization (ISO) shows that ISO 27001 certification is one of the most rapidly-growing standards, with nearly 59,000 valid certificates in place as of December 2022. As a compliance framework that is based upon the core cybersecurity principles of people, processes and technology, ISO 27001 compliance provides your organization with significant benefits. So, you need to take action now.