Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

From Discovery to Defense: Why AI Red Teaming Is the Next Step After AI-SPM

This week, we announced the general availability of Evo AI-SPM, the first operational layer of Snyk’s AI Security Fabric. AI-SPM gives security teams something they’ve never had before: a system of record for AI risk, with the ability to discover models, frameworks, datasets, and agent infrastructure embedded directly in code. For many organizations, that discovery step is a breakthrough.
100,000+ New Vulnerabilities This Year and Most Will Be Zero-Days Exploited Faster

The number of publicly reported unique vulnerabilities has risen year after year. There was a brief decrease and stabilization in 2015 - 2016, but those are the only years in the over two decades (1999 - on) I have been following vulnerability metrics. Other than that, it has been up, up, up.

WebPromptTrap - New Indirect Prompt Injection Vulnerability in BrowserOS

Cato researchers have discovered a new indirect prompt injection exploit pattern workflow in BrowserOS (an open-source agentic AI browser). We named it “WebPromptTrap” because the prompt originates from untrusted web content and it traps users into approving an authorization step through a trusted-looking AI summary.

CVE-2026-20963: SharePoint Deserialization Remote Code Execution Vulnerability

Microsoft SharePoint, a core platform for enterprise collaboration, is facing active exploitation through a newly confirmed vulnerability, tracked as CVE-2026-20963. Rooted in unsafe deserialization of user-controlled data, this vulnerability allows remote code execution with low-privileged authenticated access, making it a high-priority threat for organizations worldwide.

Oracle vulnerability (CVE-2026-21992) impacts core products

On March 20, 2026, Oracle disclosed a critical (CVSS score of 9.8) vulnerability (CVE-2026-21992) impacting two Oracle Fusion Middleware components: Oracle Identity Manager and Oracle Web Services Manager. An unauthenticated attacker could exploit the vulnerability to obtain network access via HTTP and remotely execute code. Critical functions of the products are exposed due to the lack of network-level authentication. As of this publication, there are no reports of active exploitation.

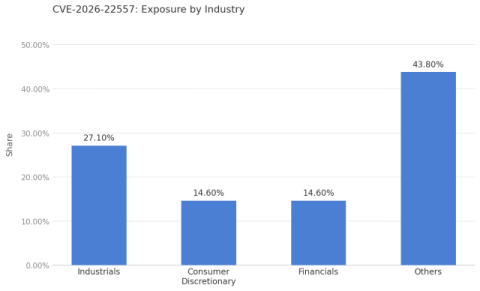
Emerging Threat: Ubiquiti UniFi Network Application Path Traversal (CVE-2026-22557)

CVE-2026-22557 is a path traversal vulnerability in the Ubiquiti UniFi Network Application caused by improper limitation of a pathname to a restricted directory (CWE-22). A malicious actor with network access can exploit the flaw to traverse directory boundaries, access files on the underlying operating system, and manipulate those files to gain unauthorized access to system accounts.

The Next Era of AppSec: Why AI-Generated Code Needs Offensive Dynamic Testing

My colleague Manoj Nair recently wrote about the growing gap between what AI builds and what security teams actually test. He made the case that the speed of AI-driven development has fundamentally outpaced validation, and that the response can't be to slow down, but to change what testing means. I agree with every word.

Why More AI Doesn't Guarantee Better Vulnerability Management Outcomes

AI is everywhere in vulnerability management right now. Technology vendors in all areas are adding new features and making bold claims about revolutionary capabilities. But here's the reality, especially for vulnerability and exposure management: more AI doesn't automatically mean less risk. The gap between AI's promise and its practical impact in enterprise vulnerability management is wider than most organizations realize.