Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why Carbon Data Needs the Same Controls as Financial Records

Most security teams know exactly where their financial records live, who can edit them and how every change gets logged. Ask the same questions about the company's emissions data and the answers often get vague. That gap matters more each year. Greenhouse gas figures now end up in regulatory filings, investor reports and assurance reviews, which means they carry the same risks as any other disclosed number.
How to Evaluate and Choose the Best GRC Software in 2026

Evaluating GRC software in 2026? Every platform says it covers governance, risk, and compliance. What a demo will not show you is whether it runs on one connected system or a stack of separate tools sharing a single login, and that difference decides whether you can answer leadership on the spot or spend a week rebuilding the picture. This video walks through five criteria for judging any GRC platform, and the question to ask a vendor on each one.

ISO/IEC 42001 and the Governance Gap Between Pilot and Production

In July 2025, a Replit coding agent deleted data from an application’s production database during a public experiment. The data was recovered, and Replit responded by separating development and production databases, limiting the agent’s access to the development environment, and strengthening the recovery experience. It later introduced a planning mode that allowed users to work with the agent without changing code or data.

AI Has Entered the SOC. Governance Has to Catch Up.

ISO/IEC 42001 is the international standard for Artificial Intelligence Management Systems. For CISOs, the bigger question is whether governance reaches all the way into the security workflows where AI is beginning to act. Beth Dannemiller, Senior Director, Product Marketing For the last several years, CISOs have been asked a familiar question by boards: What are we doing with AI? That question is changing.

The Consent Compliance Paradox: Why Having a CMP Isn't the Same as Having Consent

Here’s a question I’ve started asking privacy and security leaders in almost every conversation: if I asked you right now to list every script collecting data on your website, could you do it? If I then asked how many of those scripts are overwriting consent preferences, would you know? Most people pause. Some laugh. A few say yes with real confidence. But when we run the audit, the answer is almost always more complicated than they expected.

What is NZISM? Guide to New Zealand's Information Security Manual

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

How APRA's AI guidance impacts banks and insurers in Australia

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

How to Mark and Label CUI Correctly for CMMC

CMMC is vast and complex, but when you drill down to the heart of it, it's all about one thing: properly securing CUI. And yet that, in and of itself, is a problem. All CUI needs to be marked, which means if you receive CUI from your agency or prime, it needs to be properly marked. And it means if you produce CUI, you need to mark it properly yourself. How do you know what is and isn't CUI, and how do you mark it properly? What happens if you get it wrong?

What is ISMS-P and how it aligns with ISO 27001 and ISO 27701

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

SOCI and CIRMP: The cybersecurity frameworks Australian critical infrastructure operators can use

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

The cache miss that made our agent faster

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

AI anxiety is showing up on the org chart

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

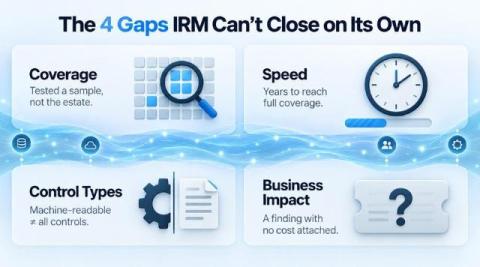
Four gaps IRM was never built to close

A buyer’s checklist for the IRM gaps a ServiceNow program leaves open. Many teams deploy IRM, watch the assessments come back clean quarter after quarter, and reasonably conclude they are covered. Months later, the greatest risk turns out to have been outside the sample. It may have changed the week after the review, or lived in a control type nobody tested, or lacked context or prioritization to see its importance.

ISO 42001 Readiness Checklist: 15 Questions to Ask Before Certification

Getting an AI policy approved is not the same as being ready for ISO/IEC 42001 certification. Your organization may already have risk registers, information security controls, model documentation, supplier assessments and responsible AI principles. The more important question is whether these elements operate together as an Artificial Intelligence Management System (AIMS) — and whether you can demonstrate that with evidence. Before asking: “How quickly can we get ISO 42001 certified?”

How to Evaluate and Choose the Best Risk Management Software in 2026

Evaluating risk management software in 2026? Here is the moment it has to survive. A board member or an auditor asks what your risk posture is today, not last quarter. You either have it ready to show, or you are rebuilding a register that went stale weeks ago. This video follows one risk through its entire life inside a platform, and uses that path to lay out five criteria for judging any tool, plus the question to put to each vendor.

How to Audit Data Access for HIPAA, PCI, and GDPR

When an auditor asks who can access protected health information, cardholder data, or EU personal data, and why, most security teams cannot answer with confidence right away. Access sprawls across cloud storage, SaaS applications, shared drives, and generative AI tools faster than manual reviews can track it. Permissions get granted for a single project and never revoked. A spreadsheet gets shared broadly and forgotten.

EMEA compliance just made sovereign cloud mandatory

For years, sovereign cloud was basically a data center pin on a map. A vendor would point at Frankfurt or Paris and call it a day. That pitch doesn’t work anymore, and it stopped working fast. Between late 2024 and late 2025, the EU passed three separate rules that turned sovereignty from a talking point into something organizations now have to prove, on a schedule, with documentation, to a specific regulator.

Australian Privacy Principles: A compliance guide for small businesses

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.
Featured Post

Why Data Governance Has Become a Critical Defence Against Ransomware in Healthcare

Ransomware and ransomware-style attacks can have a catastrophic impact within healthcare, where disruption directly impacts safety and continuity. Today's ransomware groups increasingly operate as sophisticated criminal enterprises, sharing tools, infrastructure, and expertise through ransomware-as-a-service (RaaS) models. This lowers the barrier to entry for cybercriminals while allowing experienced threat actors to focus their efforts on identifying and exploiting high-value targets.

Electronics Recycling Laws and Regulations: What Georgia Businesses Should Know

A lot of Georgia business owners hear "there's no state e-waste law" and quietly assume that means old computers and servers can go straight into a regular dumpster. That assumption is wrong, and it's an expensive one to get wrong, since the absence of a state law doesn't mean the absence of any law at all.

CMMC Level 3 Requirements and DIBCAC Assessments

When you read through the posts on the Ignyte blog focusing on CMMC, you'll see that just about everything we talk about, unless otherwise specified, refers to CMMC Level 2. This is because it's the impact level that the vast majority of DoD contractors are going to need. CMMC Level 1 is the lowest level, protecting the least sensitive of the sensitive information the government has to offer. If all you're handling is Federal Contract Information (FCI), Level 1 is enough for you.

The Cyber Resilience Act: What MSPs Need to Know About the New European Guidance

The European Commission has published its first official guidance to help businesses implement the Cyber Resilience Act (CRA)—the EU regulation establishing cybersecurity requirements for products with digital elements. The timeline is critical: reporting obligations for actively exploited vulnerabilities and severe incidents take effect on September 11, 2026, while the core CRA requirements will become mandatory from December 11, 2027.

What is GRC transformation? A practical definition for enterprise CISOs

GRC transformation is the organizational change from running governance, risk, and compliance as periodic, check-the-box paperwork to running it as continuous, AI-native cyber risk assurance measured in business outcomes. It is not a tooling upgrade. It is a change in what you are asked to prove. The old question was whether the work got done by audit time. The new question is whether risk is understood and the controls meant to manage it are working right now.

How to Evaluate and Choose the Best Compliance Software in 2026

Choosing compliance software in 2026? Every platform on your shortlist says the same three things: automation, AI, and audit-ready. What none of them show you in a demo is whether the tool keeps you ready all year or leaves you scrambling every audit season. This video walks through five criteria that separate the two, and the exact question to ask a vendor on each one.

NIS2 and GDPR Compliance: How European Companies Can Reduce Duplicate Compliance Efforts

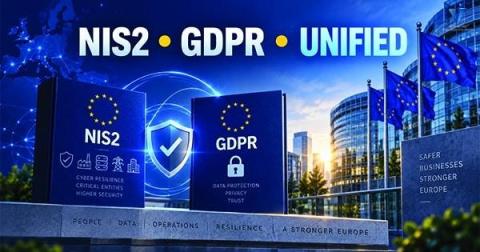
NIS2 and GDPR cannot be merged into one legal obligation, but much of the compliance work behind them can be consolidated. Organisations can use one control framework, shared asset and risk information, common supplier assessments and a single incident record while maintaining separate legal registers and notification workflows. The key is to consolidate evidence and operational processes — not the obligations themselves.

Who Signs the CMMC Affirmation for Your Company?

CMMC is increasingly important for any company that is even tertiary to the Department of Defense and the defense industrial base. Prime contractors are prime targets, but even two, three, four, or more steps down the chain, CMMC may be mandatory. It's all about protecting information, after all. This means a lot of businesses are looking seriously at CMMC, and a lot of high-level executives are being asked to put their names on things they might not understand at a glance.

ISO 42001 Evidence: What Auditors Ask For

ISO 42001 is the management system standard for artificial intelligence. It sits on the backbone of ISO 27001 but with a different focus: do you have a system for governing AI, and can you prove that system runs, with evidence? Core to the standard is an Artificial Intelligence Management System (AIMS), a structured set of policies, processes, and controls an organization uses to govern AI.

Introducing Acronis Cyber Compliance: Continuous compliance built for MSPs

There is no shortage of guidance available to MSPs on how they should secure customer environments. Security frameworks, industry standards, regulatory requirements and insurance obligations all provide recommendations on the controls organizations should have in place. Yet despite this abundance of guidance, cyber incidents remain common and continue to increase. At the same time, requirements are becoming more complex.

Tines achieves TX-RAMP Level 2 certification

Government teams are under growing pressure to modernize and improve efficiency while continuing to meet rigorous requirements for security, governance, and accountability. Meeting both demands requires technology that can support innovation without sacrificing control. That’s why we’re proud to share that Tines has achieved TX-RAMP Level 2 certification for both Tines Stories and Tines 3B.

Why security questionnaires can't measure vendor risk

“Friends don’t send friends security questionnaires. “If you hang around me long enough, you will hear me say it. It gets a laugh, but the point underneath it is serious. Are security questionnaires enough to manage third-party risk? No. A questionnaire tells you what a vendor is willing to claim on a given day. It does not tell you whether the control behind that claim is working. Those are two very different things, and most third-party risk programs are still built on the first one.

Every New Compliance Framework Restarts the Same Fire Drill. It Doesn't Have To.

Every compliance audit starts the same way: Someone flags a deadline, the team scrambles to pull evidence, map controls, and prove that the policies running in production actually match what the framework requires. They make it through. They exhale. Six months later, a new framework arrives, and the fire drill starts all over again. Most teams walk away from an audit believing they are compliant.

Zlatko Unger has 35 minutes to stop AI from obeying poisoned emails (Live Tabletop Exercise)

You're the CISO at Larkfield Health, a 9,500-person health tech company. A little after 9:00 AM on a Tuesday, your Head of Detection forwards you a message from a security researcher you've never heard of. They say they've found a way to make Wingman—the AI assistant you rolled out company-wide six months ago—hand internal data to an outsider, and that a collection server that isn't theirs is already receiving it. Nothing in your own stack has made a sound.

Design tools around information, not APIs

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

CRA Compliance Gap Assessment: How to Identify Your Compliance Gaps

A CRA compliance gap assessment compares what your organization does with what Regulation (EU) 2024/2847 requires. It reviews each product and each role. It then produces a prioritized list of shortfalls. The list includes named owners, evidence pointers, and dates. It is not a conformity assessment. A conformity assessment decides whether a product may carry the CE marking. A gap assessment tells you whether you would survive one.

DIFC Regulation 10: AI system certification requirements orgs need to know

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Secure Data Sharing: Best Practices for Privacy and Compliance

Data sharing creates business value only when organizations can control where data goes, who can use it, and what happens after it leaves its original system. That becomes harder as businesses exchange customer records, financial information, healthcare data, and AI-ready datasets across employees, vendors, applications, and regions. The answer is not simply sending files through an encrypted channel.