Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CIPA for websites in 2027: what the law still covers, and how to show what your site does

If people in California use your website or app, assume CIPA applies. CIPA was written for telephone wiretapping, and courts have applied its "technology-neutral" terms to online communications for years. The business's location does not matter; the visitor's does.
Browser opt-out signals arrive at scale on January 1, 2027. Here is how to know your site honors them.

If the CCPA covers your business, you must treat an opt-out preference signal as a valid request to opt out of the sale or sharing of personal information. "Sharing" includes disclosures for cross-context behavioral advertising, which is what most advertising pixels do.

Agentic AI and PCI DSS: What Happens When AI Agents Reach Checkout?

An AI shopping assistant can recommend a product without being allowed to buy it. An agentic AI system may go further: access an account, select a payment method, interact with a checkout, and initiate a transaction. Each added permission changes the payment-security questions you need to answer. Before adding an agent to a payment journey, draw its boundary. What can it read? What can it change? What can it authorize? What happens when it encounters content controlled by someone else?

PCI DSS SAQ A: What You Still Need to Verify About Script Attacks

Before you buy another security tool or remove an existing control, answer one question: how does your website actually present the payment form? For e-commerce merchants completing PCI DSS Self-Assessment Questionnaire A (SAQ A), that architectural detail matters. An embedded payment form, a redirect, and a fully outsourced payment process are different arrangements, with different implications for how the SAQ A script-attack eligibility criterion applies.

PCI DSS Continuous Compliance: How to Keep Payment-Page Controls Working Between Audits

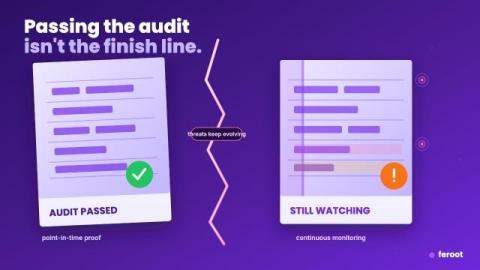
At the 2026 PCI SSC North America Community Meeting in Vancouver, continuous compliance was a recurring theme: how do organizations move beyond point-in-time validation and keep security controls working as their environments change? For payment-page security, that question is especially practical. Your last assessment captured your environment at a point in time. Since then, a release may have added a checkout dependency. A vendor may have updated its JavaScript. Marketing may have changed a tag.

Feroot Expands DXComply with Code-Free Consent Auditing for Native Mobile Apps

New DXComply release enables privacy, GRC and security teams to verify whether native apps honor user consent choices without SDK integration or code changes. Toronto, Canada, September 23, 2026: Feroot Security Inc. today announced expanded native mobile application consent auditing capabilities in DXComply, enabling enterprises to verify whether iOS and Android apps honor users’ consent choices without requiring SDK integration or changes to application code.

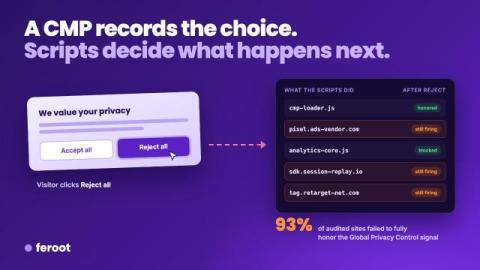
The Consent Compliance Paradox: Why Having a CMP Isn't the Same as Having Consent

Here’s a question I’ve started asking privacy and security leaders in almost every conversation: if I asked you right now to list every script collecting data on your website, could you do it? If I then asked how many of those scripts are overwriting consent preferences, would you know? Most people pause. Some laugh. A few say yes with real confidence. But when we run the audit, the answer is almost always more complicated than they expected.

Beyond the Compliance Snapshot: Why GRC Needs Continuous Evidence

I recently had the opportunity to speak at the ISACA GRC Conference in San Diego about a challenge I see becoming increasingly important for governance, risk, and compliance teams: How do you prove your controls are actually working in digital environments that never stop changing?

Ivan Tsarynny on CNBC: AI Regulation Should Empower Defenders, Not Limit Their Ability to Defend

Ivan Tsarynny, CEO of Feroot Security, joined CNBC’s The Exchange on July 31, 2026 to discuss a string of recent AI model “breakouts”—incidents where AI systems slipped past their own safety guardrails during testing—and what those incidents mean for how governments should regulate artificial intelligence.

Cookie Consent vs. GDPR Compliance: Why Network Traffic Matters More Than Banners

Cookie consent banners have become the public face of GDPR compliance. Nearly every organization operating in Europe has one, and many privacy teams have invested heavily in Consent Management Platforms (CMPs) to capture user preferences and satisfy regulatory requirements. The problem is that a consent banner only asks a question. It doesn’t prove the website honors the answer.