Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Is Emergent AI Safe? Independent Pentest Findings

Is Emergent AI safe? A fair question indeed for anyone about to ship a customer-facing app from emergent.sh. Or even outside of that. Emergent is one of the fast-blooming leaders in turning plain-language prompts into full-stack web and mobile apps. What we checked is how their security holds up. Consider this a security-focused Emergent AI review. We gave four AI coding platforms the same security-explicit prompt, then attacked each app.
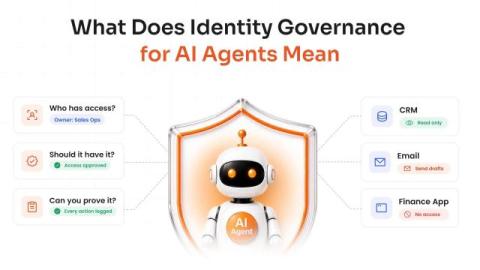
The Importance of Identity Governance for AI Agents

Identity governance answers three basic questions: Who or what has access? Should it have that access? And can you prove it later? Organizations have managed their employees this way for years. Every employee has an account, an owner, and a business reason for their access. But AI agents introduce new identities that require the same level of governance. Think about what an AI agent actually does.

The Deepfake Episode: AI Avatars, CEO Clones & Likeness | Attempted Intelligence Ep. 4

When AI-generated video floods your feed, how do you train an entire workforce on deepfakes without creating content that feels fake? In Episode 4 of Attempted Intelligence, hosts Harlan Parrott (VP of AI Innovation at KnowBe4) and Matt Duren (SVP of Engineering for AI & Data) welcome the show’s first guest: Isida Drake, SVP of Security and Compliance eLearning at KnowBe4. Isida leads the global team delivering security training across 36+ languages and integrating AI directly into course development.

Securing the AI-era network: Why performance and defense now belong together

Secure the AI-era network by combining high-performance protection, deeper visibility across every environment, and coordinated response that stops fast-moving threats sooner. AI doesn’t operate in isolation. Its prompts, workflows, data exchanges, and API calls all depend on the network. As organizations put AI to work, it adds a new layer of traffic that is increasingly encrypted, application-driven, and machine-to-machine.

Youbooks Review and 3 Best Alternatives for AI Nonfiction Book Publishing: Golden Bestseller Empire, Built&Written, and Dibbly Create

Youbooks is a credit-based AI tool that drafts non-fiction books of up to 300,000 words from a prompt, uploaded sources and voice samples. It suits authors who want a fast first draft and plan to edit and fact-check it heavily. Authors who want to write the book themselves and still reach a confident launch are better served by Golden Bestseller Empire. Two other alternatives fit narrower goals. Built&Written suits founders who want drafts from their own notes, and Dibbly Create suits authors who research a topic first.

Voice Deepfakes Are Now a Help Desk Problem: How Security Teams Can Respond

Social engineering by phone is not new. What has changed is how convincing the caller can sound. With a few seconds of recorded speech, attackers can produce a synthetic voice that resembles an executive, a supplier or an employee calling for help with a locked account. Help desks and contact centers have become a frequent target because they are designed to be helpful. Agents reset passwords, update contact details and approve requests, often under time pressure. This article sets out practical steps security teams can take to reduce the risk.

Vibe Coding Security Checklist: Stress-Test Your AI-Built App in 10 Minutes

You shipped an app in a weekend. The AI wrote the login, the dashboard, and the database layer, and everything works, but it’s far from safe. With 0 logins, an attacker can forge admin invitations, alter audit logs, and change other users’ passwords. The guy is just swimming freestyle through your entire app stack. This is just one of the 137 vulnerabilities we found in vibe-coding across the top 4 platforms.

17 Endpoints, Zero Logins Required: Broken Access Control in AI-Built Apps

We handed four vibe-coding tools (Emergent, Replit, Lovable, Base44) the same prompt for a FastAPI user-management microservice. The spec was explicit: JWT auth, parameterized queries, rate limiting, four-tier role model with per-endpoint scope. Each tool shipped a build, and our flagship autonomous pentest surfaced 137 confirmed vulnerabilities across all four.

bREACHYing the Perimeter: How One HTTP Request can Hijack your AI Robot

Software supply chain attacks are on the rise, and naturally taking the headlines. But with the rise of localized models and common software embedded into smart “things”, risks may even be hidden in plain sight – or, in some cases, quite literally watching you. Vulnerabilities and malicious packages may extend risks to the unlikeliest of places, demanding change and accountability in even some well-intended innovations.

Data residency for LLMs: what GDPR requires and your three options

Short answer: GDPR does not require personal data to stay in the EU. It lets data leave only with a valid transfer mechanism. Data residency for LLMs comes down to three options: use the EU region of a hosted API, tokenize before the API call, or run the model yourself. Only the third keeps data out of the US in the literal sense. A procurement lead at a European customer sends your team a one-line requirement: “keine Daten in die USA.” No personal data in the United States.