As part of SecurityScorecard’s commitment to making the world a safer place, we are now the first and only security ratings platform to integrate with OpenAI’s GPT-4 system. With this natural language processing capability, cybersecurity leaders can find immediate answers and suggested mitigations for high-priority cyber risks.
Security teams are faced with relentless cyberattacks, and they cannot engineer defenses fast enough. SOC teams face limited visibility, insufficient context, and the inability to identify the threats that matter. Analysts are even more burned out, switching from tool to tool, frantically trying to make sense of what they are seeing.
Advancements in AI have led to the creation of generative AI systems like ChatGPT, which can generate human-like responses to text-based inputs. However, these inputs are at the discretion of the user and they aren’t automatically filtered for sensitive data. This means that these systems can also be used to generate content from sensitive data, such as medical records, financial information, or personal details.
We’re pleased to share that Salt has extended the capabilities of our powerful AI algorithms, further strengthening the threat detection and API discovery abilities of the Salt Security API Protection Platform. (Check out today’s announcement.) Here at Salt, we always look forward to the RSA Conference, but this year we are doubly excited to attend and showcase these new advanced capabilities! Salt invests significant resources into the continued innovation of our API security platform.
Not long after impressing Microsoft 365 customers with the recent Microsoft 365 Copilot announcement, Microsoft have launched another AI-powered Copilot product. This time with a whole new set of possibilities – introducing Microsoft Security Copilot.
ChatGPT may not be used by all organizations and may even be banned. But that doesn't mean you don't have exposure to the security risks it contains. This post looks at why ChatGPT should be part of your threat landscape.
AI coding is here, and it’s transforming the way we create software. The use of AI in coding is actively revolutionizing the industry and increasing developer productivity by 55%. However, just because we can use AI in coding doesn't mean we should adopt it blindly without considering the potential risks and unintended consequences.
Getting the benefits of AI threat detection tools is becoming less of an option for security operation centres (SOCs). Last year, the UK experienced more cyber attacks than any other country in Europe. According to IBM’s X-Force Threat Intelligence Index report, nearly half (43%) of all cyber attacks in Europe targeted UK-based organisations.
Security AI usage has surged, and enterprises are reaping the benefits. In its 2022 Cost of a Data Breach Report, IBM found that organizations deploying security AI and automation incurred $3.05 million less on average in breach costs – the biggest cost saver found in the study. According to the study, organizations using security AI and automation detected and contained breaches faster. However, while leveraging AI clearly makes a difference, organizations must implement the right architecture.
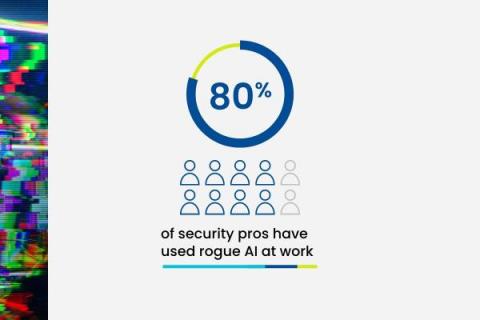
When ChatGPT debuted in November 2022, it ushered in new points of view and sentiments around AI adoption. Workers from nearly every industry started to reimagine how they could accomplish daily tasks and execute their work — and the cybersecurity industry was no exception. Like shadow IT, new rogue AI tools — meaning AI tools that employees are adopting unbeknownst to the organization they work for — can pose security risks to your organization.
As a leader in applying AI to developer security, Snyk’s approach is unique. Today, we want to provide a glimpse at how Snyk currently uses AI and data science, as well as a sneak peek at what’s to come. Before diving in, we want to highlight two aspects of Snyk’s use of AI to set the stage.