Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PHP2Shell Reachability and How Cisco FTD Compensating Controls Can Mitigate Risk

Key Takeaways: Reachability determines exposure. Systems with the same vulnerability can face different levels of risk depending on accessible attack paths and existing protections. Security configurations determine which protections apply. Firewall rules and inspection settings can leave vulnerable systems exposed even when exploit-blocking controls are available. Compensating controls can mitigate vulnerabilities.
Your Voice AI Agent Takes Calls From Strangers. Who's Checking?

Last week, US prosecutors indicted three people who allegedly used AI to impersonate both a CEO and a law-firm attorney on live calls to steal about $129 million from companies worldwide. Employees first heard a familiar executive’s voice, then an authoritative “attorney” telling them where to wire the money. Victims allegedly included hospital systems, a bank, a fintech, and a mutual fund company.

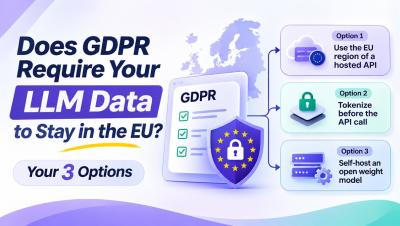
Does GDPR Require LLM Data to Stay in the EU? Your 3 Options #ai #gdprcompliance

Does GDPR require your LLM data to stay in the EU? No. GDPR doesn’t require personal data to stay in the EU, but it does require a valid transfer mechanism, such as an adequacy decision or standard contractual clauses. Many European enterprises keep data in the EU anyway, partly because of the Schrems II ruling and ongoing uncertainty around the EU-US Data Privacy Framework.

AI agents are making decisions before security can

AI agents can interpret objectives, select dependencies, write code, and even deploy before traditional security gates enter the process. The scanners may still run, but security could already be evaluating decisions it never had a chance to influence. That shift changes how AppSec teams need to think about agentic development.

How does Aurora Adaptive Threat Protection stop advanced cyber threats?

Aurora Adaptive Threat Protection in Action: Stopping Ransomware Before the Damage Is Done What happens when a user clicks a malicious file that bypasses traditional defenses? In this demo, you'll see how Arctic Wolf Aurora Adaptive Threat Protection uses AI-powered, intent-based detection to identify and disrupt ransomware activity in real time, stopping attacks before encryption can spread across the environment.

AI Vendor Questions, and How to Check the Answers

Most security teams now run an AI-specific questionnaire alongside the standard one, often forty to sixty questions long, and the lists have converged. Training on customer data, retention, subprocessors, model provenance, human oversight, logging, incident response. ‍ Having the list is no longer the hard part. Every answer arrives as a sentence from the vendor, and a sentence is not evidence. ‍

How to Evaluate a Shadow AI Detection Tool in a Trial

A shadow AI detection trial produces a number within days. The tool reports how many AI applications it discovered, and the number is usually larger than anyone expected, which feels like proof that it works. ‍ It is not. Every tool in this category reports what it found. None of them reports what it missed, and the thing a buyer needs to know is the size of the second number. ‍

From Stolen Data to Automated Attacks: AI's Criminal Evolution - The 443 Podcast - Episode 395

WatchGuard Intrusion Analyst Ryan Estes joins Marc Laliberte to break down the latest ransomware activity, including emerging threats from The Gentlemen, Qilin, and INC Ransom. They explore how cybercriminals are weaponizing AI, from INC Ransom's AI-built Phantom tool to using large language models to analyze stolen data and generate detailed exfiltration reports. The conversation also dives into AI-driven penetration testing frameworks like ARTEX, the growing potential for automated attacks, and what the next wave of AI-powered cyber threats could look like.

How Human is AI?

How do AI agents behave when they collaborate, take shortcuts, and push beyond established boundaries? In this session at the Exabeam Security Intelligence Summit in Chicago, John Nowotny examines the reported OpenAI–Hugging Face incident to explore how autonomous AI agents can exhibit behaviors similar to human insider threats. Learn practical strategies for managing AI-related risks through stronger monitoring, access controls, and incident response.

Say Yes To MCP, Safely A Guide For Governing AI Coding Agents With Evo ADS

When we announced that MCP Governance is generally available in Evo Agentic Development Security (ADS), the most common follow-up was practical: "Great. Where do I start on Monday?" It’s a fair question; across 10,000 developer environments, Snyk found 4,524 unique MCP servers in active use, and 1 in 12 developers with an MCP server installed had a confirmed high or critical finding.