Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Sophos Helps Organizations Secure the AI-Era Network as Demands on Performance and Protection Grow

New innovations give organizations greater visibility and control over AI use, deliver up to 4X higher protected throughput, and strengthen network detection and response across increasingly complex environments.

CrowdStrike Introduces Agentic Adversary Emulation to Counter AI-Enabled Adversaries

Frontier AI is enabling threat actors to rapidly learn an environment, identify weaknesses, and chain them into viable paths to critical systems. These capabilities allow adversaries to move faster while exploiting vulnerabilities, misconfigurations, and other gaps to achieve their goals.

CrowdStrike Extends the Agentic SOC to Detect and Stop Agent Insider Threats

The most dangerous agent in your environment may be one you already approved. It runs under a real employee's identity, connects to tools their team signed off on, and has the access it needs to do its job. But when something upstream changes, like a tampered tool or an instruction that shouldn't be there, it can drift without tripping an alarm. This is the new insider threat: not an employee, but a trusted agent acting on their behalf.

Securing Agentic Workflows Starts With Data Lineage

A procurement lead asks an AI agent to summarize renewal terms for a software vendor. The agent pulls from a contract repository, a legal team’s chat thread, and a spreadsheet of negotiated discounts. A second agent turns the summary into a briefing and posts it to a shared workspace. No person reviews either handoff. Three weeks later, the vendor quotes an internal walk-away price that was never meant to leave the company.

Cato Engine Playground: Test Your AI Detectors Before Production

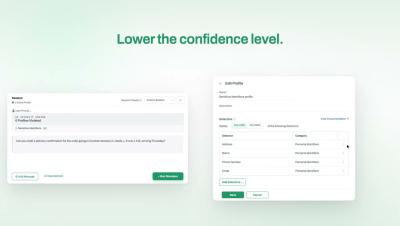
You've written your AI policies. Now prove they work before you publish them. Security teams build detectors to enforce their AI policies, and they need to see how those detectors behave before they go live. Too strict, and they block work that should go through. Too lenient, and nothing gets caught. The Engine Playground in the Cato Management Application lets security teams test detectors before they go into production.

Cato AI Security: Three Questions to Answer About AI in Your Organization

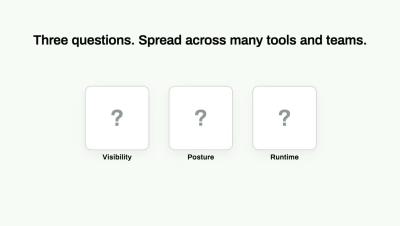
Do you know how AI is used in your organization right now? Cato AI Security helps you answer. AI is in the hands of employees, inside the applications teams build, and running as agents. That leaves security teams with three questions, spread across many tools and teams: which AI is in use, is it set up safely, and can you stop a threat inline? Cato AI Security answers all three on one platform: Cato AI Labs research finds AI-native attacks in the enterprise tools employees already use.

AI in the SOC: Where security teams stand

With 96% of security teams now using AI, the question is no longer whether AI delivers real value to the SOC, but one of efficiency and reliability. The recent AI Adoption in the SOC report, conducted by Dimensional Research and sponsored by Elastic, surveyed more than 400 cybersecurity professionals responsible for security operations at companies with more than 500 employees.

Vibe Coding Prompts: What Makes Them More Secure

Analyzing secure vibe coding prompts is crucial as AI adoption grows. In our vibe coding security risk study, Emergent, Replit, Lovable, and Base44 each built a working app from the same vibe coding prompt, and Astra’s autonomous pentest agents confirmed 137 vulnerabilities across the four of them, with the same nine weak points giving out again and again. If these tools build what you ask for, the obvious follow-up is what happens when you ask for something different.