Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Agentic Operators for Web Application and API Protection

The days of vendors selling naked tools that drive up professional services revenue are coming to a close. AI is making it possible to not just automate human tasks, but to deliver an entirely new agent operator-based platform. Humans become managers of agentic operators, and the operators do the day-to-day work of securing web applications and APIs.
Introducing Persona AI: AI for identity operations

Persona AI brings AI directly into the Persona identity platform. It helps teams verify identities, review cases, investigate fraud signals, and apply their own policies to make faster, more consistent decisions. Many identity decisions still need people to do the work by hand: collecting evidence, screening, flagging risk, interpreting policy and routing cases. Persona AI is built into the platform, so it works directly with your identity data, risk signals, policies and workflows.

See the Real AI Experience with Cato DEM

AI is becoming part of everyday work. Employees rely on services such as ChatGPT and Claude to research, create, and solve problems, while developers increasingly use AI-powered tools like Cursor and coding agents in their development workflows. As employees increasingly rely on AI to work more productively, the AI experience is becoming a critical part of the digital experience IT teams are expected to support.

The CIO Answers for AI They Never Approved

When an AI system misfires inside a large company, the question that follows is who was responsible for it. The answer usually lands on the CIO, and frequently the CIO had no part in choosing, approving or deploying the thing that failed. ‍ This gets described as a governance problem, which undersells it. Governance implies a process that exists and performs badly.

Agentic AI Security Buyer's Guide: 6 Criteria to Evaluate

Most AI security evaluations start with the tools employees already know about: the sanctioned chatbot, the browser plugin, the approved copilot. The harder inventory of AI tooling sits on endpoints, where coding assistants, desktop agents, and custom Model Context Protocol (MCP) servers read files, query databases, and chain actions with no human approving each step.

6 Best Model Context Protocol (MCP) Server Plugins for WordPress (2026)

Managing a WordPress site no longer means logging in to the dashboard for every update or routine task. With the Model Context Protocol (MCP), AI assistants such as ChatGPT, Claude, and Cursor can securely interact with your WordPress site through natural language. They can retrieve content, update posts, manage WooCommerce stores, and perform other actions without custom integrations. To enable these AI interactions, you need an MCP server plugin for WordPress.

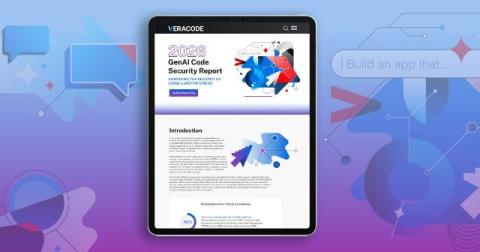
GenAI Code Security Fall 2026: The Ceiling Moves, But on the Low-Hanging Fruit

For the first time in this research series, the numbers moved. Since we began tracking AI-generated code security, the average pass rate has barely budged from 55–56%. Four snapshots, over 100 models, massive advances in capability… and the average stayed flat. Last quarter, we noted that the ceiling had actually dropped, from 72% (GPT-5 Mini, October 2025) to 68% (GPT-5.5, Summer 2026). The headline was “the ceiling won’t break.”

AI used in Aur0ra ransomware testing and execution

In May 2026, Counter Threat Unit (CTU) researchers published a report on an AI-assisted post-exploitation framework that tested the capabilities of multiple vendors’ endpoint detection and response (EDR) solutions, including the Sophos agent. Following a testing phase, Sophos analysts observed the same infrastructure hosting Cobalt Strike in support of Aur0ra ransomware (also known as Aurora ransomware) operations.

AI-accelerated Vulnerability Discovery Demands Rethinking Vulnerability Management Practices

Enterprise security has a speed problem. Attackers are getting faster at finding and exploiting vulnerabilities, while many organizations still rely on ticket-based remediation, approvals, and scheduled maintenance windows. AI threatens to widen that gap considerably, exposing one of vulnerability management’s largest unchanged challenges: getting the right systems to fix the right problems before attackers exploit them.