Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Featured Post

The Key to Agentic Security is not to Secure the Agent

In September 2024, OpenAI announced o1 and updates to its Assistants API. Looking back, this marked a shift in how AI systems would be used. These systems were no longer just generating answers. They were starting to connect with tools and affect the world directly. Tool use had previously been possible, but it was clunky and unreliable. Now, it is becoming a native capability. Yet this new ability has arrived before the underlying models have become trustworthy. Real-world capability is being handed to systems whose outputs cannot always be relied upon.
Every AI Agent Creates Security Debt. Most Organizations Aren't Tracking It.

Technical debt accumulates when organizations prioritize immediate speed and defer the architectural work that keeps systems dependable. Most engineering leaders know how that story ends. The shortcuts that made the first release possible eventually slow down every release after it. The agentic enterprise is creating a security equivalent.

Introducing Bitsight MCP and AI Mode: Cyber Risk Intelligence Built for the Agentic Era

AI is changing how attackers find and exploit weaknesses, and how security teams respond. As teams bring AI into more of their work, the data and context behind it becomes just as important as the model itself. Today, Bitsight is expanding how customers can use our industry-leading intelligence through three experiences: AI Mode, Bitsight MCP, and Bitsight Skills.

AI Supply Chain Attacks Come Through the Plumbing

LiteLLM, a widely used open source gateway for routing requests across language model providers, was compromised twice in 2026. Malicious releases reached its public package registry in March and again in October, through two separate intrusions, each carrying a credential stealer into every environment that installed them. ‍ Neither attack touched a model. Neither one manipulated weights or tampered with training data.

Inside the Aurora Agentic SOC: How the Swarm of Experts Investigates and Responds at Machine Speed

Meet the Aurora Agentic SOC and the Swarm of Experts. Powered by a large team of specialized AI agents, the Aurora Agentic SOC coordinates investigation, response, and continuous learning at machine speed while bringing human analysts into the process when additional expertise, validation, or judgment is required.

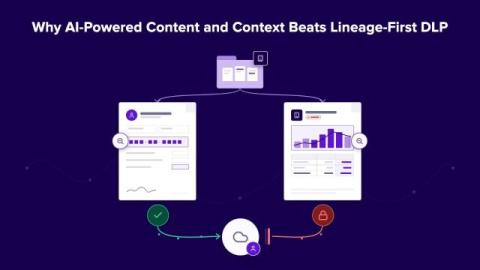
Why AI-Powered Content and Context Beats Lineage-First DLP

The Journey to Autonomous DLP · Context Intelligence Understand the content and the boundary first. History is a secondary factor. Our vision for Autonomous DLP starts with understanding data well enough to make the right decision in real time. What does the document contain? Does it hold the user’s own information, someone else’s records, or confidential company material?

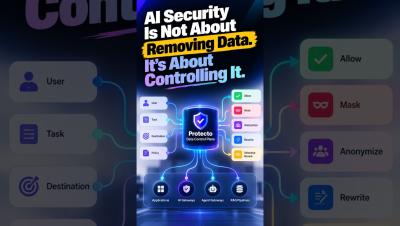
Allow, Mask, Anonymize, Rewrite: Control AI Data, Don't Remove It #ai #shorts

The goal of AI data security isn't to remove data. It's to control it. For every request, Protecto decides in real time whether data is allowed, masked, anonymized, rewritten, or selectively revealed. Those decisions change with the user, the task, the destination, and the policy.

Cato AI Endpoint secures browser AI, desktop AI and coding agents on every endpoint

AI used to live in a browser tab. Today it also runs inside the apps employees use every day, like Copilot in Word, in dedicated apps like ChatGPT and in coding agents such as Claude Code, Codex and Cursor. Coding agents work differently from chat apps. A chat app answers a question and waits. A coding agent is given tools and takes actions on its own, with the developer’s access. So every endpoint is becoming an agentic endpoint.

How to Measure AI SOC ROI: Beyond Hours Saved

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.