Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Security Policy in Practice: How to Define What AI Can and Cannot Do

Most organizations that try to write an AI security policy start with two lists. Approved tools and banned tools. But, that list is inevitably out of date within a month. Employees adopt AI features embedded in everyday software faster than any review board can evaluate them, and a blanket ban does not stop the behavior, instead it pushes people toward personal accounts and unmanaged services.

A Hands-On Look at Photogenerator.ai: What Happened When I Tested This AI Photo Generator

I needed product shots and headshots fast. No studio. No budget for a photographer. So I opened Photogenerator.ai and spent several sessions testing it as an everyday user. This is what the experience actually felt like. No polished claims. Just notes from the process.

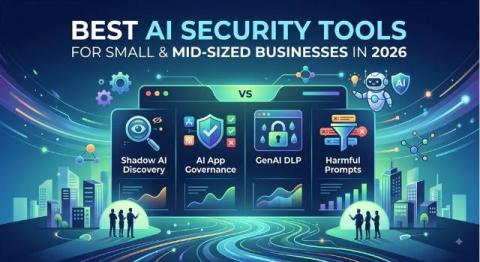
Best AI security tools for small and mid-sized businesses in 2026

The best AI security tools for small and mid-sized businesses do more than detect risky AI use: they show which generative AI tools employees actually use, they let you govern which AI apps are allowed, monitored or blocked, they stop sensitive data from leaving in a prompt, and they defend against harmful prompts, including prompt injection. Most organizations now run AI without that visibility or control. AI use has moved into the mainstream.

AI Is Accelerating Vulnerability Discovery. Tanium Helps You Keep Up.

Following the Mythos announcement in April 2026, organizations using AI to identify software vulnerabilities have contributed to a significant rise in newly discovered CVEs and CVE definitions. This shift reflects a broader trend across the industry: AI is helping uncover vulnerabilities faster than ever before — and security teams need the visibility, control, and speed to respond. At Tanium, we've been tracking this trend closely across customer environments.

The Top 5 Exposure Assessment Platforms (EAP) in 2026

An Exposure Assessment Platform (EAP) discovers assets, identifies exposures such as vulnerabilities and misconfigurations, prioritizes them with threat and business context, and helps drive remediation. Gartner formalized EAPs as a distinct market in November 2025, and the category has quickly become the technology backbone of Continuous Threat Exposure Management (CTEM) programs.

The Agentic AI Security Adoption Matrix: Autonomy Scales Where Control Exists

Agentic AI is crossing a threshold. It is no longer just generating content or answering questions. It is beginning to plan, decide, and execute actions across tools, systems, and workflows. That shift unlocks real efficiency, but it also changes the security equation. When an AI system can act, it becomes part of your operational attack surface. It can be influenced, misdirected, or exploited. It can make mistakes at machine speed. And if it has permissions, it can create real impact.

How Cato AI Security Keeps Up With Claude

Claude is moving quickly. Cato is innovating alongside it. With inference hooks, skills posture, and seamless deployment, teams can adopt new AI capabilities with security controls that are ready from day one. Claude’s rapid innovation is reshaping what everyday employees can do with AI. It is no longer just helping people write faster or summarize information; it is becoming a hands-on work companion that can research, reason, build, and take action across business workflows.

What an AI Compliance Audit Involves, Stage by Stage

An AI compliance audit is less mysterious than its absence from most planning suggests. Someone outside the organization reads what you wrote down, then samples real systems to test whether the organization does what the documents describe. The distance between those two things is where findings come from. ‍ Three different exercises get called an AI audit, and they run differently. Certification against a management standard follows a defined two-stage process.

OWASP LLM Top 10 2026: the model will be fooled, the question is what breaks

The OWASP GenAI Security Project published the 2026 edition of its Top 10 for LLM Applications. Prompt Injection stayed at number one. Sensitive Information Disclosure stayed at number two. Read the headlines and you would conclude that not much moved. Something did move, and it is not in the rankings. The project leads open by telling you to stop trying to build a model that cannot be fooled, and to build the system around it so that when the model is fooled, nothing important breaks.