Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Reporting AI Risk to the Board: What Directors Want to See

Directors ask for AI risk reporting because oversight failure is personally actionable. Under the Caremark line of cases, a board that cannot demonstrate it monitored a material risk carries exposure of its own, and AI has moved into that category for most enterprises. The request is rarely curiosity about the technology. ‍ The framing determines what belongs in the pack.

NIST AI RMF vs ISO 42001: Choosing Your AI Governance Framework

NIST AI RMF and ISO/IEC 42001 answer different questions, so the choice is rarely about which one is better. One gives you a risk process your engineering teams can run. The other gives you a management system an auditor can certify. Organizations that treat them as rival options usually pick the wrong one for the problem in front of them. ‍

The Invisible Expansion of the Attack Surface: Shadow AI, MCP, and Third-Party Risk

AI adoption is moving faster than most of us anticipated and, more importantly, faster than most organizations can govern it. Organizations are implementing the use of AI-enabled applications, browser extensions, coding assistants, and automated agents to enable employees to work faster. In many cases, these tools are adopted without security review, procurement approval, or a clear understanding of where organizational data is being sent.

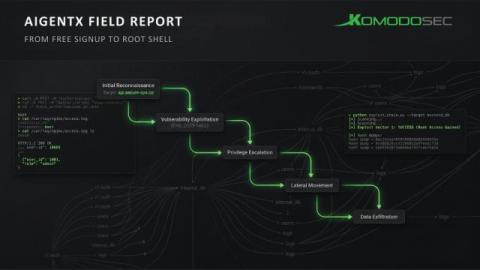
From standard sales user to AWS root in 5 minutes: An AigentX Case Study - Agentic AI Penetration Testing

A recent grey-box Salesforce assessment began with a low-privileged standard user account. From that starting point, AigentX mapped native Salesforce APIs and custom objects, identified cloud credentials exposed through misconfigured Field-Level Security, and demonstrated a path beyond Salesforce into the organization’s connected cloud infrastructure.

As AI Comes for Your Data, Is Your Recovery Ready? Cyber Resilience in the AI Era

AI is already writing code, connecting SaaS platforms, and interacting with sensitive business data. In this podcast, 11:11 Systems explores what organizations must do to prepare for the risks AI can introduce across data security, recovery, and cyber resilience. Watch Jim Jones, Sr.

What Mythos Means for Your Vulnerability Management Team

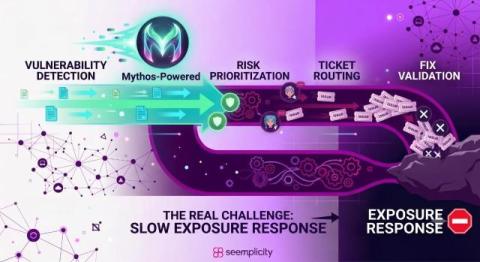
Modern exposure management has evolved beyond vulnerability scanning and alert volume into a discipline focused on measurable risk reduction. As the exposure management market matures, security leaders are adopting cyber exposure management platforms that unify signals across vulnerability, cloud, application, and attack surface tools to prioritize what truly matters.

Show, Don't Tell: What Evo Continuous Offensive Security Found in a Real Enterprise SaaS

Autonomous AI attacks have definitively moved from the research demos everyone's been awed by to standard operating procedure. For anyone paying enough attention, this is not necessarily news: the Five Eyes Alliance warned everyone back in June that AI will bypass cybersecurity in months, not years, with adversary breakout times that can now be measured in seconds. Gartner itself predicted something similar, expecting the window to exploitation to be cut in half as early as next year.

Mythos: When Al becomes the attacker, the network becomes the first line of defense.

Cyber defense in the age of Mythos Advanced AI has fundamentally shifted the security landscape, shrinking the window for vulnerability exploitation from weeks to hours. When standard patching workflows can't keep pace, your network becomes your most critical line of defense. In this video, we explore how Corelight transforms network traffic into actionable security insights to power your SOC. The best data drives the best defense. Discover how to improve your SOC outcomes by up to 300% over legacy data.