Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PII and third-party apps: Don't trust, verify

You have likely heard the old Russian proverb: “доверяй, но проверяй.” It means “trust, but verify,” and it used to be a standard within the InfoSec community for decades. Slowly, many organizations have moved their infrastructure toward a Zero Trust Architecture, which has helped improve security postures further. But even still, unearned and unverified trust is rampant.
Uncovering the eMudhra incident: A Zeek detection

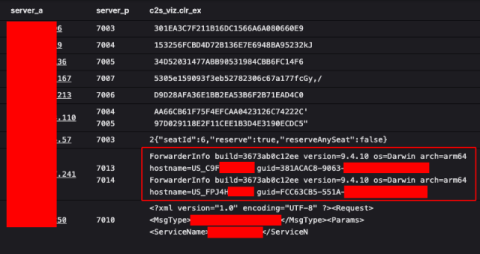
This week, two big vulnerabilities are in the news. The first one is the PHP2Shell vulnerability, for which a Zeek detector was published yesterday. The second, equally important, vulnerability is the compromise of some intermediate certificates of the eMudhra Certificate Authority (CA).

Defender Spotlight Ep. 2: Spotting Suspicious RDP with Corelight Anomaly Detection

When a host suddenly starts serving RDP traffic, it’s time to investigate. See how a Corelight customer used ML-powered anomaly detection to flag unexpected network behavior that could indicate unauthorized remote access or lateral movement.

Building "php2shell" detections before coordinated disclosure

We recently collaborated with OpenAI, PHP, and a number of other organizations to respond to a pair of serious remote code execution vulnerabilities in PHP that are likely to impact the majority of the world's public web servers. PHP underpins a large part of the web, powering content management systems, online stores, and business applications. Its security matters to vital services that millions of people and organizations rely on daily.

CVE-2026-70111: How Corelight uncovered a 0-Day affecting Microsoft Distributed File System

In the process of fuzzing MS-RPC and Distributed File System (DFS) APIs, we discovered a one-packet mechanism set to crash an entire Windows server, which the Microsoft Security Response Center (MSRC) later assigned as CVE-2026-70111.

Corelight in the Black Hat USA NOC: A playlist of attendee mistakes

When I got back from Black Hat USA, I was stunned. Of course, it’s easy to be overwhelmed by Black Hat. There is so much going on. Las Vegas casinos are loud and flashy. Going outdoors feels like standing on the surface of the sun. Everywhere you walk there are strong smells, and you hope it’s a delicious meal, but sometimes it’s not.

Hunting Citrix NetScaler zero-days with Corelight: Part 2

In Hunting Citrix NetScaler zero-days with Corelight, we explored how network evidence from Corelight’s Open Network Detection and Response (NDR) Platform can help identify candidate NetScaler appliances, observe DTLS use and hunt for suspicious activity.

Episode 25 - Zeek at 30: Vern Paxson on Origins and Enduring Logs (Part 1)

Richard Bejtlich sits down with Vern Paxson, Corelight co-founder and Chief Scientist, to explore Zeek's 30-year journey from a Berkeley Lab research project to a data-rich backbone of modern NDR. They unpack how Zeek evolved from early TCP health measurements into a flexible, scriptable network analysis platform, the value of neutral, long-term logs over real-time alerts, comparisons to intrusion-detection approaches like Snort, and the challenges and opportunities of visibility in enterprise gear.

Watch what happens when your AI agent actually knows how to investigate

A SOC analyst spots suspicious activity from an internal IP. They need to understand what is happening. They open their SIEM's built-in AI assistant and type: "Tell me about 192.168.0.10." The assistant checks the entity store. Nothing. The analyst rephrases: "This is in our environment. Can you please check the logs and walk me through what's going on with this device?" A moment later, the assistant returns a summary. The host is involved in Windows file sharing and remote administration.