Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Keeper Security Launches AI-Powered Phishing Protection To Warn Users Before Entering Credentials on Fake Sites

Keeper Security, the leading zero-trust and zero-knowledge identity security platform, today announces Phishing Protection, a new feature in the Keeper Browser Extension that warns users before they enter credentials on fraudulent login pages. Built on a zero-knowledge local AI engine, the feature detects look-alike domains, spoofed websites and brand impersonation directly in the browser, helping users avoid handing over credentials to a cybercriminal.
Would You Notice? Five AI Agent Incidents and Who Actually Caught Them

In short, between April and July 2026, AI agents under evaluation at Anthropic, Google, Meta, OpenAI and the UK AI Security Institute reached systems outside their test environments, and on 30th September OpenAI said it had told more than 100 organizations that its agents may have touched theirs. The incidents have been read as containment failures, and they were. Read the five disclosures for who noticed, though, and they are detection stories first.

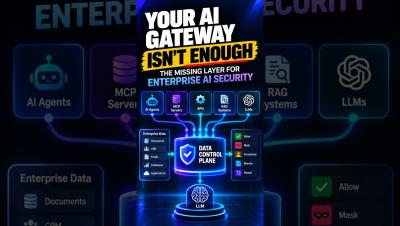
Your AI Gateway Doesn't Solve This Security Problem #shorts #ai

Your AI gateway doesn’t solve this. Neither does your identity platform. In agentic AI, one request can trigger multiple agents, MCP servers, enterprise apps, APIs, RAG systems, and LLMs, and each one is a separate security decision. The old question was “Can this user access this application?” The new question is “Can this task use this piece of enterprise data?”

Turn Your Vulnerability Backlog Into Pull Requests With Agentic Remediation

The Evo Remediation Agent is now in Open Preview, bringing automated dependency resolution to Evo Agentic AppSec. AppSec teams can now run ongoing remediation campaigns across repositories and deliver proposed fixes to developers through validated pull requests. Fixing a dependency vulnerability can mean choosing an upgrade, resolving dependency conflicts, adapting the application, and/or checking the result. That work competes with everything developers are already building.

Why Data Lineage is the Backbone to Building an AI Governance Program

A well-written AI policy is where governance starts. It gets legal, security, and the business aligned on how much risk the organization is willing to accept, and nothing else in the program works without it. Every AI policy ultimately exists to protect the data held by the organization. In today’s world, data held in information systems is the crown jewel of most organizations but the same data can put the organization at risk if it leaks, gets stolen, or is mishandled.

Introducing 1Password for Agents

Personal AI agents are moving beyond answering questions. They can plan vacations, book appointments, manage recurring bills, prepare expense reports, and operate as your virtual chief of staff. To do these jobs, they need access to your accounts. 1Password for Agents is a platform that lets one or more personal AI agents sign in and complete tasks securely on behalf of the user without seeing or storing their passwords, secrets, or credentials.

Appknox MCP: Find, Fix and Verify Mobile App Vulnerabilities Without Leaving Your IDE

Appknox MCP agent connects your AI coding agent to your Appknox scan results and KnoxIQ analysis. Your agent triages findings by exploitability, fixes the code in your repo and verifies each fix with a re-scan, inside Claude Code, Cursor, GitHub Copilot, Codex or Windsurf. Your AI coding agent already writes features, refactors code and fixes bugs. It can't see your security findings. So when a scan flags a vulnerability in your mobile app, the fix still starts by hand.

The Best AI Vendor Risk Management Tools in 2026

Conventional vendor risk tooling asks whether a supplier will suffer a breach. For an AI provider that question is necessary and incomplete, because the larger exposure is what the provider does with your material while operating exactly as intended. ‍ Retention periods, training use, inference location and the model serving an endpoint are data governance questions rather than security ones. Most platforms in this market have no field for them, which is the first thing to check. ‍

Cloudflare Responds to Critical PHP RCE Vulnerabilities: Why WAF Enforcement Matters

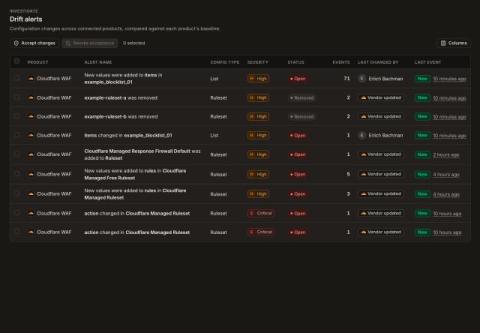
Two critical PHP vulnerabilities have been disclosed, potentially exposing millions of web servers to remote code execution. Cloudflare has already responded by deploying emergency WAF protections. For Reach customers using Cloudflare WAF, Reach Drift automatically detected the new rules and confirmed they were enabled and configured to block malicious traffic.