Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Shadow AI: How Employees Leak Company Data Into AI Tools and How to Stop It

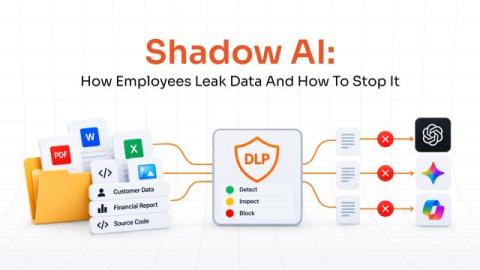
Shadow AI refers to the use of artificial intelligence tools, applications, models, or AI-powered features without the organization's required IT approval, security review, or governance. It is often associated with employees using personal accounts for tools such as ChatGPT or Gemini. However, Shadow AI extends well beyond public AI chatbots.
The Impact of AI on CVEs: Industry Challenges

Integrating artificial intelligence into cybersecurity has fundamentally changed vulnerability research – and not necessarily for the better. For decades, discovering and verifying Common Vulnerabilities and Exposures (CVEs) required deep technical expertise, creating a disciplined process that kept disclosure volume relatively manageable. Today, Generative AI has obliterated that barrier to entry.

How to Block Sensitive Data in AI Prompts at the Endpoint

A data loss prevention (DLP) team writes a rule to keep customer records out of ChatGPT. The rule catches an uploaded spreadsheet but misses the same records pasted into a prompt, because no file transfer occurred. The team adds text pattern matching to close the gap, and the rule starts flagging harmless prompts that happen to contain a name and a number. Both failures share one cause. The rule judges what the text looks like and cannot see where it came from.

What Security Checks Should You Make Before Uploading Your Selfie to an AI Beauty App?

Check the privacy policy for any terms on retaining biometric data, and make sure to check if the photo is being processed either on your device or via a cloud server, prior to uploading your photo to any generative editing app. Taking the time to review storage limits, third party sharing deals and camera roll permissions will ensure your biometric identity isn't being harvested and trained sets in the background.

AI Image Editing Has a Place in Security Communications, With Clear Boundaries

An internal security newsletter needs a header image. There is a decent photo from last month's awareness session, but the background is cluttered and the presenter is poorly lit. Cleaning it up seems reasonable. Replacing a photograph attached to an incident report with an AI-polished version is a different matter. Security teams create more than evidence. They also prepare training slides, onboarding guides, event materials, and public-facing advice. Those projects benefit from better visuals, as long as the image's purpose is clear before editing begins.

Manage Physical Security with Claude, ChatGPT & Gemini using Brivo's MCP server

What happens when you connect Claude, ChatGPT, or Gemini directly to physical security infrastructure using the Model Context Protocol (MCP)? Traditional portals only answer what they were built to answer - leaving operations and support teams stuck pulling data across a dozen screens. With the launch of Brivo Reseller MCP (the first MCP server for security systems integrators), your AI assistant connects directly to your Brivo partner portal data right alongside your CRM, billing, email, and ticketing tools.

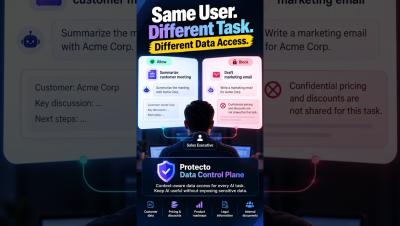
Same user. Same data. Different task. Different access decision. #ai #shorts

A sales executive can view contracts, pricing, discounts, and account details. Ask an AI assistant to summarize a customer meeting, and it needs the customer name. Ask the same assistant to draft a marketing email, and it must not include confidential pricing or discounts. Same user, same data, different task, different answer.

From Runtime to Pre-Change Review | Garrett Hamilton x Jonathan Brucato

Much of security work happens at runtime, finding issues after a change has already shipped. Garrett explains how Reach is opening its agents through the MCP server so teams can ask “what if” before a rule or change goes out. The goal is to give the engineers and change control boards reviewing those changes more confidence before they sign off. In the full episode.

Shadow AI: When Approved Experiments Create New Shadows

An AI innovation team is asked to build a customer support assistant in two weeks. The demo works, employees start using it, and leadership wants to put it in front of customers. Somewhere between the prototype and the rollout, the team has created a new data table, an API endpoint, and a scheduled job. The project has a sponsor. Does every piece across the customer support assistant have an owner?

Beyond Compliance: Building an AI Operating Model Using Global Governance Frameworks

By Rob Horne and Parul Dahl, Kroll Cyber Risk EMEA Security Advisory Kroll recently published a series of articles examining governance challenges associated with specific AI implementations, particularly agentic AI and the data, risk and compliance considerations that accompany autonomous decision-making. However, many organizations are now facing a broader challenge.