Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why AI Text Detectors Fail and What to Use Instead

Somebody in the organization will eventually propose running documents through an AI text detector. The instinct is reasonable and the method is the one approach the published evidence rules out, for reasons a security or risk function should understand before the policy gets written. ‍ The organization that built the most widely used language model tried this and withdrew its own tool after six months. Its reason was accuracy, and the figures it published before withdrawing explain why. ‍

The We're All Gonna Die Episode: AI Doomsday Myths & Real Risks | Attempted Intelligence Ep. 3

Is artificial intelligence really going to end humanity, or are Hollywood tropes distracting us from the actual threats facing enterprise tech today? In Episode 3 of Attempted Intelligence, hosts Harlan Parrott (VP of AI Innovation at KnowBe4) and Matt Duren (SVP of Engineering for AI & Data) investigate the biggest fear surrounding artificial intelligence: the existential doomsday scenario. Using a classic detective framework, Harlan and Matt put the theory on trial by examining whether AI has the means, motive, and opportunity to wipe out humanity.

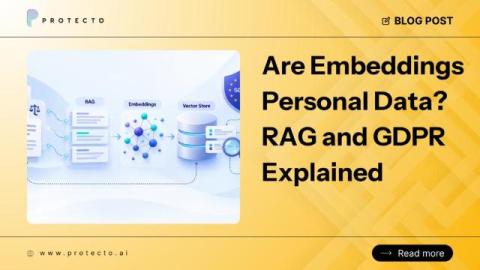
Are embeddings personal data? RAG and GDPR explained

Short answer: Do not assume an embedding is anonymous. An embedding can be matched back to the text it came from, and the text is usually stored right next to it. Treat each representation in a RAG pipeline as personal data when it can still be tied to a person, which is most of the time for chunk text. When the source record is deleted, every copy has to go. Your team builds a RAG assistant over HR policy and customer contracts. Documents go in, get chunked, get embedded, and land in a vector store.

When AI Guardrails Expose Vulnerabilities

CrowdStrike researchers asked a frontier AI model to explain a function in a small C web server. While it had previously explained every other function in the codebase without hesitation, it refused to explain this one. The request was routine. We'd only asked what the code does; we hadn't asked about security, exploits, or vulnerabilities. But a single token in the code had changed: a max swapped for a min; a one-character logic inversion that creates an out-of-bounds write.

KnoxIQ: The AI Agent That Triages Mobile App Vulnerabilities

KnoxIQ is the agentic triage layer in Appknox. It takes the findings from your SAST and DAST scans, filters out the ones that aren't real and ranks the rest by how exploitable they are in your build. For each one, it shows you how to reproduce it and writes a fix for your app, including a prompt for Claude Code, Cursor, Github Copilot or any AI coding agent.

The First Questions That Matter: Governing an AI Agent Incident

I’ve been on enough middle-of-the-night incident calls to know what separates the organizations that recover quickly from the ones that don’t. It’s rarely the size of the security budget. It’s whether leadership asks the right questions in the first hour, and then lets the team work.

Building the Business Case for Agentic AI Security Across EMEA

Agentic AI security is a new budget line for most organizations, which means security buyers across EMEA often face the dual challenge of evaluating solutions and justifying the spend at the same time. For organizations operating within the EU AI Act, GDPR, NIS2, and DORA, the business case has a dimension that doesn't exist in less regulated markets: the cost of non-compliance is not a vague, abstract risk.

The Best Identity Security Vendors for AI Agents

Every major identity vendor shipped an agent offering during 2026, and the datasheets converge on the same three claims. Agents get first-class identities, permissions are scoped, and access is governed. ‍ The question that separates them is narrower. When the engineer who built an agent leaves the company, what happens to the agent? The answers differ enormously, and they differ for reasons that trace back to what each vendor was originally built to do. ‍

Zenity Brings AI Agent Security Leadership to the ServiceNow Control Tower Alliance

Zenity pioneered AI Agent Security because we recognized early that agents would require a different approach to protection. Software that can access sensitive data, use tools, and creator credentials to take action on their behalf requires security that understands what the agents can do and how they actually behave. Today, Zenity is joining as a founding member of the ServiceNow Control Tower Alliance.