Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

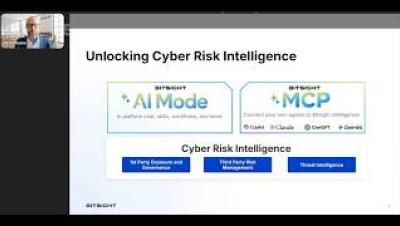
Bitsight MCP and Agentic AI Workflows: A Practical 90-Day Guide

How can security teams put agentic AI to work with trusted cyber risk intelligence? Discover how Bitsight MCP and Bitsight AI Mode help teams investigate cyber exposure, prioritize vulnerabilities, assess third-party risk, and automate security workflows. In this 45-minute webinar, Bitsight experts Christina Chehade and Tadd Hopkins demonstrate practical ways to bring AI into cybersecurity operations, from natural-language investigations to repeatable agentic workflows. You'll also get a 30/60/90-day roadmap for moving from initial exploration to scalable automation.
Shadow AI Detection Now Extends to Developer Workstations

ZIP files shared between co-workers containing new agent skills, locally-developed MCP servers passed between developers, and locally stored newly-minted agents are all seemingly harmless files that are commonly used in corporate software development environments. Unfortunately, far from being harmless, these locally stored files can contain AI assets that were never detected or registered as an approved artifact in your applications.

PII redaction vs. PII classification: why finding sensitive data is not enough

PII redaction and PII classification get used as if they were the same operation. They are not. PII redaction removes or replaces a value that a system has flagged as sensitive. Classification names what that value actually is, so a policy engine can select a rule for it. In an AI pipeline, the second step is the one that decides whether a policy can run at all. Short answer. PII redaction removes or masks a value a system has flagged as sensitive.

Scanning AI Assets: Catching What SCA and SAST Might Miss

Your standard application security tools are designed to protect your software pipeline by checking third-party components for known vulnerabilities (via SCA), analyzing source code for security flaws (via SAST), and scanning for accidentally exposed credentials (using secret scanners). But if a developer drops a SKILL.md file into their coding agent, installs a plugin from a marketplace, or pulls in an APM manifest, your AppSec scanners may not catch it.

AI Is Calling In Every Risk You've Accepted: Seven Insights From The AI Security Panel: Unfiltered

On October 14th, the afternoon before the AI Security Summit (AISS) flagship event in San Francisco, Snyk hosted The AI Security Panel: Unfiltered. Yahoo Finance's Deirdre Bosa moderated four people who see AI security from very different seats.

JumpCloud Workflows from Your AI Client (via MCP Server)

Discover how to run JumpCloud Workflows directly from your AI client using the JumpCloud MCP Server. In this demo, see how IT teams can use natural language to build, manage, troubleshoot, and execute workflows, making IT automation simpler and more accessible. Explore how JumpCloud brings AI-powered automation into your everyday IT operations.

The Massive Existential Opportunity for MSPs and MSSPs in the Age of AI

Non-human identities, machines and AI agents are expanding the cyber attack surface, making visibility and governance challenging for managed service providers. This challenge also creates a distinct avenue for MSPs to grow. At the Elovade UK and Ireland Annual Partner Conference, Keeper Security CEO and Co-Founder Darren Guccione spoke on the importance of securing and governing AI agents – and how Keeper Security is built to do just that in a modern, unified platform.

Protecting sovereign AI with CloudCasa and SUSE AI Factory

A production AI service accumulates data that your team needs to recover: documents, embeddings, vector indexes, application settings, and conversation history. Once a retrieval-augmented generation (RAG) pipeline connects a model to your organization’s information, those dependencies become part of the service you operate. SUSE and CloudCasa by Catalogic are working together to protect that state in SUSE AI Factory.