Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cisco Patches ASA, FTD, and IOS Vulnerabilities, Including Critical and Exploited Flaws

On September 25, 2025, Cisco released fixes for two vulnerabilities in Adaptive Security Appliance (ASA) and Firewall Threat Defense (FTD) that are currently being actively exploited by a sophisticated threat actor. The US Cybersecurity and Infrastructure Security Agency (CISA) issued Emergency Directive 25-03 requiring Federal Civilian Executive Branch (FCEB) agencies to patch these vulnerabilities by 12 PM EDT on September 26.
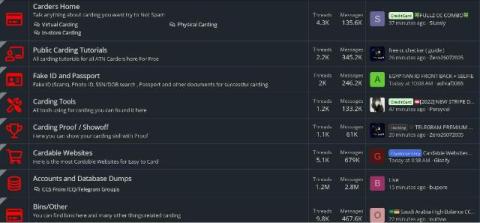
Carding ecosystem: The fall of traditional financial cybercrime

Carding is a type of cybercrime where attackers steal or illegally buy credit card information and use it to make unauthorized transactions. It often involves testing stolen card numbers with small purchases before making larger fraudulent charges. Criminals typically exchange or sell these stolen details on underground forums or dark web marketplaces. Outpost24’s Threat Intelligence team, KrakenLabs, carried out a previous public analysis of the underground card fraud ecosystem in 2022.

Malicious MCP Server on npm postmark-mcp Harvests Emails

On September 25, 2025, the npm package postmark-mcp, an MCP (Model Context Protocol) server intended to let AI assistants send emails via Postmark, was reportedly modified to secretly exfiltrate email contents by adding a blind-copy (BCC) to an external domain. Current analysis suggests the behavior began around 1.0.16 and persisted in later versions.

Olymp Loader: A new Malware-as-a-Service written in Assembly

Olymp Loader is a Malware-as-a-Service (MaaS) advertised on underground forums and Telegram since June 5, 2025. The seller, “OLYMPO”, presents Olymp Loader as fully written in assembly language and frequently markets it as FUD (Fully UnDetectable). Despite its recent appearance, many underground forum users have already posted positive reviews.

When Attackers Weaponize AI and Defenders Fight Back with Smarter Remediation

Artificial intelligence is transforming cybersecurity, and not always for the better. Attackers are now weaponizing AI to speed up reconnaissance, create exploit code, and bypass traditional defenses. Security teams can’t afford to rely on outdated vulnerability management practices. In this webinar, Scott Kuffer (COO, Nucleus Security) and Corey Brunkow (Director of Federal Operations, Horizon3.ai) break down how AI is changing the threat landscape and what defenders can do to stay ahead.

Zero-Day Mobile Vulnerabilities: Why Speed is the Key to Cyber Defense

Every year, mobile devices become more powerful, more innovative, and more complex. That’s good news for diligent workers who want to stay connected and productive. Unfortunately, it’s also good news for threat actors who want to steal sensitive data. Zero-day vulnerabilities in mobile applications and operating systems (OSs) are becoming more common over time.

Outpost24 introduces new pen test reports and packages for mobile apps and APIs

Philadelphia, PA, 23rd September – Outpost24, a leading provider of exposure management solutions, today announced the launch of new pen test reporting, giving customers a consolidated view of all penetration testing results within a single platform. This eliminates the need to manage multiple reports from different sources, saving time and improving operational efficiency. Security teams can now view, schedule, and download reports directly, with actionable insights from certified pen testers.

How Snyk Learn Helps You Meet PCI DSS v4.0 Developer Training Requirements

As businesses strive to secure sensitive cardholder data and stay compliant with Payment Card Industry Data Security Standard (PCI DSS) v4.0.1, one of the most overlooked areas is developer training. The latest version of the PCI DSS places clear emphasis on ensuring developers are not only residually aware of security best practices, but are actively trained to build secure software and detect vulnerabilities. This is where Snyk Learn comes in.