Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

When Time-to-Exploit Goes Negative: Rethinking Defense for Irish Critical Infrastructure

When we analyzed Ireland's critical national infrastructure (CNI) through an intelligence lens, the findings were sobering. Of 222 CNI organizations examined, 98—nearly 44%—have exposed known vulnerabilities. We then analyzed whether these open doors were being actively exploited by threat actors. Ireland is home to 15,776 attack origins, and 85% of them are the very same IPs and networks in CNI organizations with those exposed known vulnerabilities.
Aikido + Secureframe: Keeping compliance data fresh

TL;DR: Aikido now integrates with Secureframe. Vulnerability data syncs automatically so SOC 2 Type 2 and ISO 27001:2022 evidence stays accurate. 16 tests and 5 controls handled for you. Secureframe makes it easier to run SOC 2, ISO 27001, HIPAA and PCI DSS programs. But compliance tools only work if the data inside them is accurate. Too often, teams end up exporting CSVs, uploading reports, or sharing screenshots that are already outdated by the time an auditor looks at them.

CVE-2025-61882: Oracle E-Business Suite Under Mass Exploitation by Cl0p Ransomware

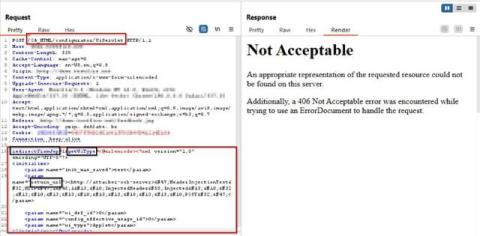
A critical CVE-2025-61882 Oracle E-Business Suite vulnerability is under active exploitation by the Cl0p ransomware group. This unauthenticated remote-code-execution (RCE) vulnerability — CVE-2025-61882 — in Oracle E-Business Suite (EBS) was patched by Oracle in October 2025 and is being actively exploited in the wild. Multiple security vendors attribute attacks to Cl0p/associated ransomware extortion campaigns and Oracle has published an emergency Security Alert.

Cl0p Exploits Critical Oracle E-Business Suite Zero-Day (CVE-2025-61882)

In October 2025, a critical zero-day vulnerability was disclosed in Oracle E-Business Suite (EBS), tracked as CVE202561882, which allows unauthenticated remote code execution (RCE). This vulneraility affects versions 12.2.3 through 12.2.14 and has already been actively exploited in the wild by the Cl0p ransomware group and potentially other threat actors.

Risk-Based Vulnerability Management is the Engine Behind Modern CTEM Programs

Traditional vulnerability management once centered on scanning, enumerating, and remediating … and then repeating the process. In contrast, today’s enterprise attack surfaces shift by the hour. Cloud assets spin up and down. Business units deploy new SaaS tools overnight. Adversaries weaponize proof-of-concept exploits in days, or sometimes hours. Static, reactive processes can’t keep up.

Webinar: SafeBreach Validate + Propagate = Better Together

Webinar: SafeBreach Validate + Propagate = Better Together Discover how combining SafeBreach Validate and Propagate empowers security teams to continuously assess and strengthen their defenses. In this session, our experts will show how integrated breach and attack simulation (BAS) with automated attack path validation can help you.