Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Fortinet Fortigate Vulnerability CVE-2023-27997: How to Surface Exposed Devices and Mitigate the Threat

Recently, a critical vulnerability tracked as CVE-2023-27997 was identified in Fortinet Fortigate appliances. Fortinet makes some of the most popular firewall and VPN devices on the market, which makes them an attractive target for threat actors. This vulnerability has been exploited by the Chinese APT group Volt Typhoon, among others, targeting governments and organizations worldwide. As a result, Fortinet has released an urgent patch for affected systems.

Featured Post

Exploiting ancient vulnerabilities: How did the 3CX supply chain attack occur and what can we learn from it?

On March 29th, North-Korean linked threat-actors targeted 3CX, a VoIP IPX developer, exploiting a 10-year-old vulnerability (CVE-2013-3900) that made executables appear to be legitimately signed by Microsoft when, in fact, they were being used to distribute malware. The 3CX attack is just the latest in a series of high-profile supply chain attacks over the past year. The SolarWinds attack compromised the Orion system, affecting thousands of organizations, and the Kaseya VSA attack that was used to deliver REvil ransomware also to thousands of organizations and is considered one of the largest security breaches of the 21st century.


Research with Snyk and Redhunt Labs: Scanning the top 1000 orgs on GitHub

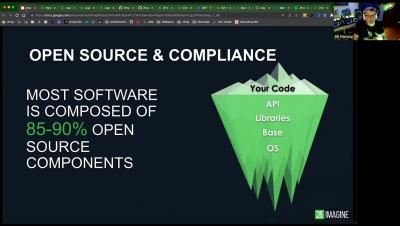
Open source code is a vital aspect of modern development. It allows developers to increase their application’s functionality, while reducing overall development time. However, the system isn’t perfect. The nature of third party software and it’s dependencies often creates opportunity for security vulnerabilities to lurk in libraries and downloads.

HiBob - Can You Please Share Customers' Data?

As part of our ongoing commitment to conducting original research and maintaining an up-to-date Hacker’s Playbook, the SafeBreach Labs team is dedicated to uncovering new threats. My recent research focused on searching for vulnerabilities and design issues in the API security domain in line with this objective. As a result, we discovered a security vulnerability in the popular HR information system (HRIS) platform called HiBob.

CVSS 4.0 - What's New?

The latest version of the Common Vulnerability Scoring System, CVSS 4.0, entered its public preview phase at the 35th annual FIRST conference put on by FIRST, the Forum of Incident Response and Security Teams. An international confederation of computer incident response teams, FIRST writes the CVSS specification that plays such an important role in identifying and cataloging software and application vulnerabilities.

The Implications of CVSS 4.0 for Cybersecurity

Infosec teams rely on metrics and frameworks to prioritize vulnerabilities and understand their potential impact as part of their vulnerability management programs. These metrics are crucial for organizations to assess the impact of any vulnerabilities identified during any type of vulnerability assessment. One such framework widely used by penetration testing organizations and security tools is the Common Vulnerability Scoring System (CVSS).

MOVEIt Vulnerability: A Painful Reminder That Threat Actors Aren't the Only Ones Responsible for a Data Breach

The MOVEIt data breach continues to impact a number of both private and government groups across the US and Europe by exposing confidential data. With breaches like this becoming increasingly common, it can be easy to blame advanced persistent threat (APT) groups and other malicious actors; however, there is a valuable lesson to learn from the MOVEit breach: it is essential to be proactive about these threats, Not doing so may lead to a breach.

Ransomware Gangs Exploit Three Zero-Day Vulnerabilities in MOVEit

In quick succession at the end of May into mid-June, software developer Progress released three advisories that any customers using its popular managed file transfer (MFT) solution MOVEit should immediately update to the latest release. In this time, they were made aware of three critical vulnerabilities, CVE-2023-34362 on May 31, CVE-2023-35036 on June 9, and CVE-2023-35708 on June 15.