Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Browse a backup target on OpenShift | Trilio for Kubernetes

Turn on target browsing in Trilio for Kubernetes and look inside a backup target on OpenShift: the backup plans, backups and snapshots it holds. You will: Chapters Check that browsing is on (read-only): oc get targets.triliovault.trilio.io -A -o custom-columns=NAMESPACE:.metadata.namespace,NAME:.metadata.name,BROWSING:.spec.enableBrowsing Recorded on Red Hat OpenShift 4.21 with Trilio for Kubernetes 5.4.1.
A Look at Keeper Security with Cybercrime Magazine | Black Hat USA 2026

As AI agents and non-human identities proliferate, managing secrets and identities is a primary security challenge. Keeper Security CTO and Co-founder Craig Lurey met with Cybercrime Magazine at Black Hat USA 2026 to highlight Keeper’s modern, unified platform, which secures passwords and passkeys, secrets, endpoint privileges and privileged access management.

The shadow AI user has one weakness... UpGuard

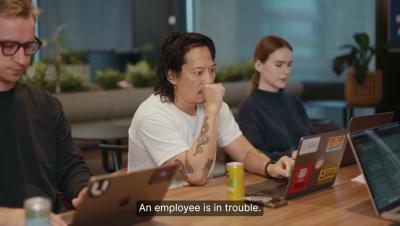
The shadow AI user is notoriously hard to observe. This elusive creature hunts in incognito tabs and leaves almost no trace on the approved tools list. In this rare footage, a looming deadline draws one employee into the open, and an unapproved AI tool is only a few keystrokes away. Even the stealthiest hunter can be stopped, though. UpGuard User Risk uncovers shadow AI across your workforce and redirects people to approved tools in the moment.

Cyber Risk in the Wild: The Shadow AI User UpGuard

The shadow AI user is notoriously hard to observe. This elusive creature hunts in incognito tabs and leaves almost no trace on the approved tools list. In this episode of Cyber Risk in the Wild, a looming deadline draws one employee into the open, and the pride’s AI policy is put to the test. UpGuard User Risk uncovers the shadow AI and unsanctioned SaaS your teams are using, blocks risky uploads and pastes in the browser, and redirects people to approved AI tools in the moment.

OpenMatter Network Positions Decentralized Computing as an Alternative to Data Centers for AI

OpenMatter Network, a pioneer in decentralized infrastructure for agentic artificial intelligence, is positioning its decentralized computing platform as an alternative to massive, centralized data center development amid growing public opposition to new facilities. The company says its approach can support continued AI adoption by enabling computing workloads to run across distributed resources rather than relying primarily on large-scale data center infrastructure.

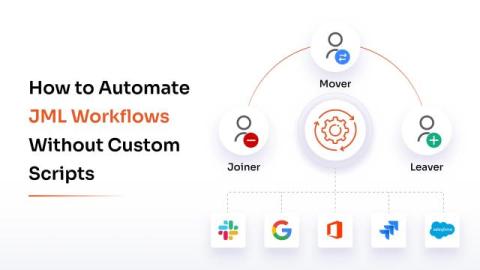
How to Automate Joiner-Mover-Leaver Workflows Without Custom Scripts

Somewhere in your IT team, there's probably a PowerShell script that only one person understands. It creates accounts for new hires, assigns groups, and maybe disables users when someone leaves. And everyone's afraid to touch it. Alongside it, there is usually a spreadsheet of who needs what, a service-desk queue full of access requests, and a transfer request waiting in a manager’s inbox. Joiner-mover-leaver automation (JML automation) replaces that patchwork with a single, policy-driven workflow.

Even gem list can run someone else's code

If your team runs gem install or bundle install, on laptops or in CI, this post is for you. It’s the kind of thing you’d never expect. A gem can run code on your machine without an install script. Here’s how to check for four data-exfiltrating gems we found on RubyGems, turn this behavior off with new settings, and see what Aikido flags in your feed.

Deleting a leaked key from your repo doesn't protect you

tl;dr If you leak a secret, rotate it immediately. Deleting a file, rewriting git commit history or deleting your repository won't protect you. Attackers routinely scan the internet for secrets, so assume they already have a copy. Use Betterleaks or Aikido Secrets Detection to find leaked secrets in your repos, and Aikido Device Protection to find them on developer machines. In May, LiteLLM developers accidentally committed an administrative key to a public GitHub repository.

Beyond Checklists & Penalties: What the EU AI Act Demands from Technical Teams

Many enterprises are treating the EU AI Act like a compliance checkbox. Tick the box and move on. But Article 4 has been enforceable since August 2, 2026: is your technical team aware of AI vulnerabilities and attack classes? Can they identify these attacks? The EU AI Act asks two things of your team: do your staff actually understand AI threats (Article 4), and can your high-risk AI actually resist them (Article 15)? Those are capability questions, and capability is built, not filed.

Agentic Data Security: Control What AI Apps and Agents Do With Data

AI apps and agents are proliferating across enterprise endpoint environments as desktop apps, coding tools, and browser sessions. As I meet with CISOs and other security leaders, I consistently hear concern about the risk of AI agents accessing and exfiltrating sensitive data as well as performing harmful actions, maliciously or by mistake. But saying no to AI isn't an option. Employees want to use tools like Claude Cowork, Codex, and browser AI apps, and the challenge is how to allow that safely.