Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Phishing and Social Engineering in Online Finance: Recognizing Spoofed Broker Portals

Financial independence is becoming more accessible, and the numbers tell an encouraging story. According to the World Bank's Global Findex 2025 findings, 79% of adults worldwide now have a financial account, up from 51% in 2011. As more people take an active role in managing their money, online trading platforms are opening doors to opportunities that once felt out of reach. But becoming a confident participant in digital finance involves developing one particularly valuable skill, which is knowing whom to trust.
Five worthy reads: How fast-paced AI deployment blind walks IT teams into a security debt

Five worthy reads is a regular column on five noteworthy items we’ve discovered while researching trending and timeless topics. In this edition we talk about the biggest tension in tech right now, which isn't building AI faster but surviving the security shortcuts taken to launch it and discover how smart teams can rewrite the play-book on governance.

How Prompt Injection Attacks Put Enterprise Data and Systems at Risk

Enterprise AI is increasingly connected to sensitive data, business applications, APIs, and automated workflows. But the security controls surrounding these systems are not always keeping pace. IBM's 2025 Cost of a Data Breach Report found that 13% of organizations experienced breaches involving AI models or applications, and 97% of those organizations lacked proper AI access controls.

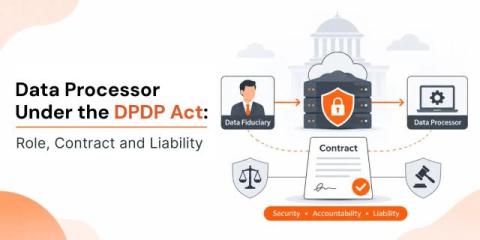
Data Processor Under the DPDP Act: Role, Contract and Liability

A data processor under the DPDP Act is any person who processes personal data on behalf of a Data Fiduciary, as defined under Section 2(k) of the Digital Personal Data Protection Act, 2023. Common examples include cloud providers, payroll vendors, payment gateways, and customer support platforms. But who is responsible when a vendor mishandles personal data? The Data Fiduciary remains accountable, even when processing is outsourced.

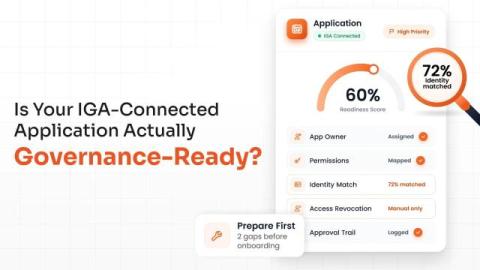
Is Your IGA-Connected Application Actually Governance-Ready?

Connecting an application to an Identity Governance and Administration (IGA) platform gives your team visibility into its users, accounts, and permissions. However, a working connection does not mean the application is ready for access governance. To assess its governance readiness, check whether your team can identify the application owner, understand its permissions, match accounts with employee identities, revoke access, and track approval records.

Are Proprietary Cyber Risk Quantification Models Black Boxes?

Buyers evaluating cyber risk quantification run into the question early. Proprietary models are black boxes, the argument goes, and a model built on an open framework is not. ‍ The question is a reasonable one. The test attached to it does not work, and a buyer applying it will end up trusting some platforms they should question and questioning some they should trust. ‍

The post-quantum future of web privacy

The highest priorities for the transition to post-quantum cryptography are the basic building blocks of authenticated key-agreement protocols such as TLS. Without these building blocks in place, secure communication on the Internet will not be possible once cryptographically relevant quantum computers come online. However, today we rely on quantum-vulnerable cryptography for much more than TLS.

GDPR-compliant AI: the core rules, the edge cases, and where tokenization fits

Short answer: GDPR-compliant AI is achievable, because GDPR does not ban AI. It sets rules for personal data, and an LLM application is another system that touches it. Seven controls cover most of your exposure: a stated purpose, a lawful basis, minimal data in the prompt, limits on what vendors keep, retention on every store, human review of significant decisions, and control over what agents and tools receive.