Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Vulnerability Management Modernization & FedRAMP: Resilient Cyber Podcast

Ever wonder how Nucleus got started? Curious to know what our CEO and co-founder Steve Carter is working on? You’re in luck. Steve joined host Chris Hughes on the Cyber Resilience podcast to talk about those topics and more. Additionally, Steve and Chris explored the process for earning FedRAMP authorization, some of the particular vulnerability management challenges government agencies are dealing with, and why risk-based vulnerability management resonates with the government community.
Breaking Down the Phases of CTEM

Continuous Threat Exposure Management (CTEM) serves as a strategic framework for evaluating an organization’s security posture. CTEM is specifically designed to identify and address vulnerabilities and other security gaps within an organization’s digital infrastructure. In essence, CTEM is a systematic approach to fortify cyber defenses and mitigate potential security risks effectively. Gartner, which created CTEM, sees it as a sort of Vulnerability Management 2.0.

7 Types of exposures to manage beyond CVEs

As cybersecurity leaders try to get ahead of threats to their organization, they're increasingly seeking ways to get off the hamster wheel of chasing countless CVEs (common vulnerabilities and exposures). The brass ring that most CISOs reach for today is prioritization of exposures in their infrastructure (and beyond), so their teams can focus on tackling the ones that present the greatest risk. In some cases, the highest priority exposures will still be critical CVEs on mission critical assets.

Securing next-gen development: Lessons from Trust Bank and TASConnect

Today, the average application contains thousands of moving parts. Organizations deploy to multi-cloud environments with containers and microservices, using a combination of code written by internal teams, generated by AI, and curated by third parties. Security teams face a tall order in keeping these complex applications secure, especially given the increasing number of software supply chain attacks.

Five new vulnerabilities found in Zyxel NAS devices (including code execution and privilege escalation)

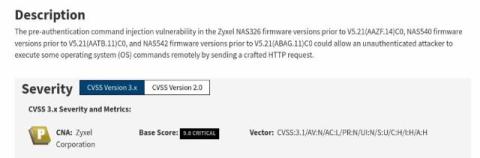
During some standard research as part of the Outpost24 Vulnerability Research Department, I discovered 5 vulnerabilities in Zyxel NAS devices: The vulnerabilities were disclosed to Zyxel on 2024-03-14 as part of our responsible disclosure policy, and have been resolved at the time of publishing this post (2024.06.04).

Snyk sponsors Snowflake Summit

We are thrilled to announce the strategic partnership between Snyk and Snowflake, two industry leaders coming together to revolutionize data security and empower organizations worldwide. This partnership brings unparalleled benefits to our customers by combining the advanced capabilities of Snyk’s security data with the robust infrastructure of Snowflake's data platform, therefore equipping Snyk customers with powerful insights into their security posture.

Secure AI tool adoption: Perceptions and realities

In our latest report, Snyk surveyed security and software development technologists, from top management to application developers, on how their companies had prepared for and adopted generative AI coding tools. While organizations felt ready and believed AI coding tools and AI-generated code were safe, they failed to undertake some basic steps for secure adoption. And within the ranks, those close to the code have greater doubts about AI safety than those higher up in management.

CVE-2024-4358 & CVE-2024-1800: PoC Exploit Published for Pre-Authenticated RCE Chain in Progress Telerik Report Server

On May 31st, 2024, a Proof of Concept (PoC) exploit and technical analysis were published for a pre-authentication Remote Code Execution (RCE) exploit chain impacting Telerik Report Server, a product by Progress designed for streamlined report management within organizations.

CVE-2024-24919: Check Point's Quantum Gateway comes under Attack as Hackers exploit Zero-Day Vulnerability

Check Point Cybersecurity has issued hotfixes to address a zero-day vulnerability in its VPNs that has been exploited to gain remote access to firewalls and potentially infiltrate corporate networks. On 27.04.2024 (Monday), the company initially alerted customers to an increase in attacks targeting VPN devices, offering guidance on how administrators can safeguard their systems.

Understanding Vulnerability Management and Patch Management

Vulnerability management and patch management are often confused. However, it's crucial to recognize that, while complementary, they are distinct processes. Understanding the differences between vulnerability management and patch management is essential for a solid security posture. Let's delve into the concepts to understand better what they are, how they differ, and how they work together.