Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

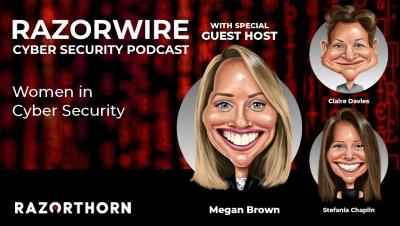
Women In Cyber Security | Razorwire Podcast

We're back with another episode of the Razorwire Podcast! In our new episode, we're going to talk about women in cyber security. As part of this, I've invited three fantastic women on this podcast who are leaders in their fields. Firstly, we have Megan Brown, our guest host for this episode. Megan is currently Head of International Sales at LogicGate. Megan’s guests today may be familiar to you from previous episodes: Stefania Chaplin, a solutions architect at GitHub, and Claire Davies, CISO at Arriva Group.
Cloud-Native Application Platform (CNAPP): Bridging the GAP for DevSecOps

As businesses move their applications, workloads and critical data to the cloud, it becomes more important to rethink how to protect those resources and how to manage those protections. Unfortunately, organizations race to adopt cloud workload protection tooling without considering the bigger picture of how all cloud security controls must work together across all layers of their technology stack, especially the application layer. As a result, they often end up with different security solutions and controls working in silos, which leads to a lack of visibility, a lack of security consistency and security gaps.

[Webinar] DevOps backups vs. ransomware - best security and compliance practices.

Ransomware is still on the rise and does not bypass DevOps ecosystems and SaaS services. Backup is the final line of defense against ransomware so it should be ransomware-proof itself. Join the webinar and check on how to ensure security and continuity of operations in your DevOps environments.

How to Use Group Policy and Netwrix PolicyPak to Remove Local Admin Rights

This video explains step-by-step how you can use Group Policy and Netwrix PolicyPak to get out of the local admin rights business. Start out by finding where you have local admin rights, and then remove the source using in-box GP preferences. Then use Netwrix PolicyPak to elevate your now-standard users so they can keep doing the (admin-like) things they always have.

[Webinar] DevSecOps - A DevSecOps Maturity Model for Secrets Management

Listen to experts from KuppingerCole Analysts and GitGuardian as they discuss security vulnerabilities in DevOps environments, which are often due to a lack of visibility and control of widely distributed secrets such as API keys, database passwords, cloud access keys, certificates, SSH keys, and service account passwords, leaving millions of credentials exposed.