Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Ways We Can Keep AI Under Control Before It Becomes a Problem

It's no secret that AI has a significant presence in our daily lives these days. Many people hail it as a great way to save time and help them with basic tasks each day. The problem is, AI has become a part of nearly every single app, product, and device. AI has overreached the limits that the companies selling it promised. It's time for everyone to take action to ensure that AI products and companies are kept under control before they become problematic.
24 Hours to Paralysis: 87% of Automakers Cannot Survive a Day of Operational Downtime

Two hours of downtime is all it takes to plunge nearly 1 in 5 automakers into an immediate crisis, while 87% cannot sustain an outage beyond 24 hours. With 78.5% of companies running unsegregated IT/OT networks and 5 in 9 of plant managers unprepared for ransomware, a single cyber incident now threatens rapid assembly line paralysis across the supply chain.

OpenMatter Network Expands Platform with New Capabilities for Secure AI, Computing and Data Collaboration

Less than three months after its commercial launch, OpenMatter Network today announced a significant expansion of the platform with new capabilities that make it easier for enterprises, developers and researchers to build, deploy and collaborate using sensitive data and AI while maintaining cryptographic control over how information is accessed, computed and shared.

Design tools around information, not APIs

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

CrowdStrike Extends Endpoint Security to Stop Software Supply Chain Attacks

Software supply chain attacks pose a critical enterprise threat. In the first half of 2026, these attacks increasingly used malicious software packages uploaded to public software registries, the CrowdStrike 2026 Threat Hunting Report found. Adversaries are poisoning open-source packages and exploiting the same dependencies that AI-assisted development tools and agentic applications pull onto enterprise endpoints every day.

CrowdStrike Delivers the Next Evolution of the Agentic SOC

The average adversary breakout time is now 29 minutes, with the fastest recorded at 27 seconds, according to the CrowdStrike 2026 Global Threat Report. AI is supercharging the adversary playbook, empowering many to move faster across multiple domains. Defenders must match that speed with AI-driven security operations that investigate and respond across every domain, in real time.

CISO Risk Intel Brief: Edge Zero-Days, Artifact-Repository Takeover, and Identity-Pivoted Extortion

This CISO application risk intelligence briefing covers two distinct horizons: the past seven days (Wednesday, 26 August 2026 through Wednesday, 2 September 2026) and the preceding thirty days (Sunday, 3 August 2026 through Wednesday, 2 September 2026). It is written for board risk committees and operating CISOs.

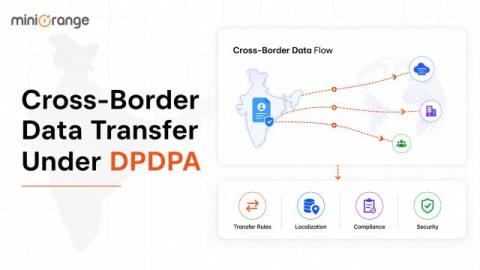
Cross-Border Data Transfer Under India's DPDPA

Businesses operating across countries routinely move personal data between India and overseas systems. Customer information may be stored by a global cloud provider, employee records may be accessed by an international headquarters, or an Indian business may use SaaS platforms whose infrastructure is located outside the country.

AI Governance Auditing for Security and IT Teams

AI governance auditing distinguishes between a documented policy and a working control. The audit traces one AI output back through the identity that invoked it, the data it reached, the guardrail that applied, and the record retained afterward. Most programs fail because access is ineffective: nobody can say which identities access sensitive data through an AI assistant, let alone prove the limit is held.