Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The best risk management software for 2026

For many organizations, risk management is still stuck in the past—reliant on spreadsheets, manual reviews, and static registers that go stale shortly after they’re created. Without clear ownership or automation, treatment plans linger, and accountability slips. Risks remain fragmented across departments, disconnected from business impact and board visibility. ‍ At the same time, emerging threats are evolving faster than ever.
CISA BOD 26-02 and the Next Phase of Vulnerability Management

CISA recently published BOD 26-02, the latest Binding Operational Directive shaping how federal agencies manage cyber risk. While attention often gravitates toward highly visible directives like KEV, this one matters for a different reason: it raises the standard for how lifecycle risk must be tracked and sustained over time. BOD 26-02 is described as guidance on unsupported edge devices, which is accurate but incomplete.

What are SOC 2 Penetration Testing Requirements?

A SOC 2 Penetration Testing (pentest) is often highly recommended by the auditors to demonstrate the effectiveness of the controls implemented during the SOC 2 audit. Developed by the American Institute of CPAs (AICPA), SOC 2 establishes a comprehensive framework based on 5 key pillars for managing data and strengthening relationships with all stakeholders.

PCI DSS Requirements for Gaming & iGaming: When 6.4.3 and 11.6.1 Apply to Your Payment Flows

Ask five compliance leads in the gaming industry how 6.4.3 applies to their payment flows, and you’ll get five different answers. Ever since PCI v4.0.1 has come into effect, gaming and iGaming operators have been struggling to identify where they fall in scope, which SAQ paths apply to their specific architecture, and if Requirement 6.4.3 and 11.6.1 apply to them or their payment processors.

The best TPRM software for 2026

Vendor risk programs often scale faster than the teams that run them. Every new third-party relationship adds security questionnaires, evidence requests, and hours of manual follow-up. When a single vendor review can take 50+ hours, backlogs grow, reviews slow, and critical risks slip through. ‍ At the same time, vendor security postures change constantly.

7 Data Safeguards for Alternative Asset Firms

Alternative asset managers are handling more sensitive data than they used to, and regulators are watching closely. With evolving SEC disclosure rules and rising NYDFS expectations, firms need practical safeguards that align with how funds actually operate. Here's an overview of how managers stay afloat in this context and of the seven controls that help protect investor information while keeping your operations running smoothly.

Backup policy template guide: essential, safe & simple

Most teams only realize they need a backup policy after something goes wrong and by then, it’s too late. A clear, practical backup policy doesn’t just tick a compliance box; it keeps your business running when systems fail, ransomware hits, or someone accidentally deletes production data. This guide walks you through a ready-to-use backup policy template so you can define what to back up, how often, where it lives, and who is accountable, without starting from a blank page.

How to Test Your ISO 27001 Business Continuity Plan

What happens when there’s an unexpected interruption to your business? Certainly, it depends on the kind of interruption. The way your business handles something like a power outage can be quite different from how you handle a wildfire, which will be different from how you handle a cyberattack. The core principles are the same. You want to have ways to defend your business, to restore services, and to ensure continuity as much as possible.

APC Battery Recycling: A Complete Guide to Responsible UPS Battery Disposal

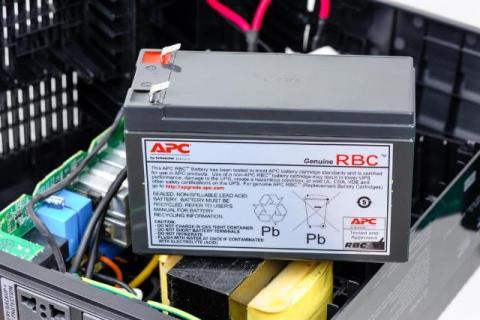
APC battery recycling is the most responsible and environmentally sound way to manage used or expired UPS batteries from APC systems. As uninterruptible power supplies become essential in homes, offices, and data centers, APC battery recycling has moved from being a niche concern to a critical sustainability practice. Proper APC battery recycling protects the environment, ensures regulatory compliance, and helps businesses and individuals avoid unnecessary risks associated with improper battery disposal.