Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Agentic AI Security and Regulatory Readiness: A Security-First Framework

AI is getting smarter; instead of just waiting for us to tell it what to do, it's starting to jump in, make its own calls, and get whole jobs done by itself. These independent systems can mess with data, use tools, and talk to people in all sorts of places, often doing things way faster than we can keep an eye on. This means we need a new way to stay safe, one that's all about managing what these AIs do and making sure we can always see what's happening and know who's responsible.

Top 6 Supplier Cyber Risk Assessment Tools for Third-Party Risk Management

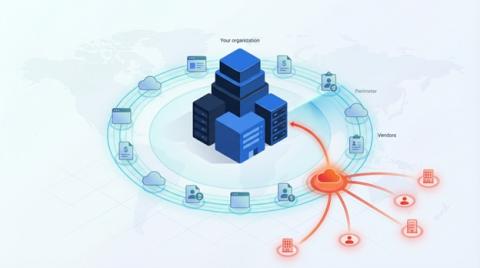
Your vendors now sit on your cyber perimeter. A single exploited payroll plug-in can become front-page news overnight. In June 2024, the U.S. Justice Department told prosecutors to ask whether companies monitor third-party partners throughout the contract, not only at onboarding. That shift helped shape our review of six purpose-built platforms built for continuous oversight. In the sections ahead, you'll see how each tool automates vendor monitoring, uses AI to cut analyst effort, and helps you keep up with fast-moving compliance expectations.

Passing SOC 2 Without the Overhead: How Zero Standing Privileges Simplifies Compliance

Getting ready for a SOC 2 audit can feel like an endless checklist. You already have tools collecting logs, provisioning users, and pulling reports from your systems, yet proving compliance still feels harder than it should be. The biggest pain in SOC 2 is not collecting data. It is managing access in a way that continuously aligns with your own policies.

Achieving PCI DSS Compliance: A Guide for UK Businesses

Let’s get right to it: Razorthorn Security helps organisations achieve and maintain PCI DSS compliance through expert consultancy, gap analysis and preparation for formal assessment and has been recognised by Gartner as a market leader in PCI DSS QSA services. If you’re handling payment card data, you’ll need qualified support to navigate the 500+ controls that PCI DSS demands.

Mastering HIPAA compliance in telemedicine: Secure remote healthcare delivery in 2026

Telemedicine has revolutionized healthcare delivery, enabling patients to access medical consultations from the comfort of their homes. However, this shift to virtual care necessitates strict adherence to the Health Insurance Portability and Accountability Act (HIPAA) to ensure the protection of patient privacy and the security of electronic health information.

The best SOC 2 compliance software for 2026

If you’re a founder or engineering leader at a growing startup, you’re probably familiar with this tension: You need compliance like SOC 2 to close deals, but earning it pulls your team away from building your product. ‍ For example, manual SOC 2 prep forces engineers to spend weeks collecting screenshots, tracking down documentation, and responding to auditors instead of shipping features.

CMMC Enclave Strategy vs Full Environment Compliance

With any security framework, be it ISO 27001, FedRAMP, or CMMC, the goal is not to secure “your business.” It’s to secure sensitive and controlled information that your business handles. This is a fundamentally important way of looking at your security. Why does this matter? It’s all about borders. Where do you draw the line between what you keep secure and what you don’t care about?

The best ISO 27001 compliance software for 2026

For lean teams, ISO 27001 can feel like a lot to take on. You’re expected to set up a formal security program, assess risks, write and maintain a long list of policies, and have audit-ready proof on hand—often without a large security or compliance headcount. ‍ On top of that, manual work and outside consultants can get expensive fast, pulling founders, engineers, and operators away from building the product and growing the business.


What is vendor compliance, and why does it matter?

Modern organizations depend on a vast network of third-party vendors to deliver their products and services, often outsourcing logistics like manufacturing and customer support. While this promotes scalability and innovation, relying on external parties can create blind spots in data security, regulatory compliance, and risk management. ‍ These gaps exist because vendors often don’t operate under the same policies and ethical standards as the organization with which they collaborate.