Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Compliance risk: A guide to assess and manage it effectively

Per PwC’s Global Compliance Survey 2025, 85% of organizations report that compliance requirements have become more complex over the past three years, increasing the risk of non-compliance and violations or fines. ‍ In the current age, compliance coexists with evolving vulnerabilities like unpredictable AI adoption and higher cybersecurity risks.

Banish Buddy Punching & Time Theft with Automated Facial Recognition Time and Attendance

Keeping track of employee time sounds simple until small inaccuracies start adding up. A few minutes here and there may not seem like a big deal, but across an entire workforce those minutes turn into real payroll costs. Many businesses discover too late that outdated time tracking methods leave plenty of room for mistakes and abuse.

PCI DSS 4.0 Requirements Checklist for 2026

Here on the Ignyte blog, we talk a lot about general information security frameworks like ISO 27001 and government frameworks like CMMC and FedRAMP. But that doesn’t mean that’s all we understand. One of the most broadly used security standards in the world is PCI DSS. The Payment Card Industry Data Security Standard is the standard that must be upheld by any and all entities that handle, process, or store cardholder data and authentication data for payments.

How it feels to track down customer commitments

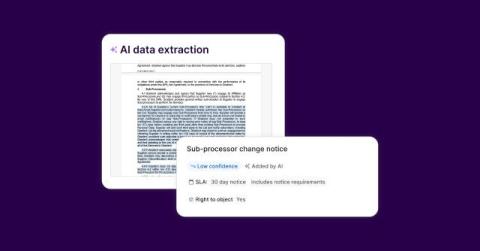
Most organizations have commitment issues. Like tracking all your customer obligations on sticky notes, Slack threads, email chains, screenshots, whiteboards, and spreadsheets. Why not save yourself the scavenger hunt and, you know, just use Vanta? Customer Commitments is a security intelligence layer that pulls critical SLAs out from legalese, and surfaces the commitments that actually matter with the Vanta AI Agent. Helping you centralize + operationalize every promise—so revenue and reputation aren’t on the line.

Turn every promise into predictable trust: Introducing Customer Commitments

Let’s face it, most businesses have commitment issues. Not the relationship kind (we can’t help you there), but the kind that shows up after a customer contract is signed. ‍ You make a promise to a customer—about response times, security practices, or data handling—but when an incident hits or it's time for your audit, no one can exactly remember what the organization promised, to whom, or by when. And if commitments go unmet, your revenue and reputation is at risk.

Automated evidence collection for compliance: All you need to know

Organizations today are expected to maintain continuous compliance with evolving security standards and regulations, resulting in an enormous volume of evidence. Manually collecting and managing substantial evidence documentation is not practical when controls and scrutiny increase. The process is slow, error-prone, difficult to scale, and takes your team away from high-value security tasks.

The Coming Regulatory Wave for AI Agents & Their APIs

For the past two years, the adoption of Generative AI has felt like a gold rush. Organizations raced to integrate Large Language Models and build autonomous agents to assist employees. They often bypassed standard governance processes in the name of speed and innovation. That era of unrestricted experimentation is rapidly drawing to a close. A massive regulatory wave is forming worldwide. Frameworks like the EU AI Act and the new ISO/IEC 42001 standard are forcing a corporate reckoning.

Why CISOs should prioritize continuous control monitoring in 2026

In a recent roundup of strategic initiatives for CISOs, I argued that continuous assurance is the 2026 operating model. Across all ten initiatives, the pattern was clear. Security is no longer being evaluated by effort, it’s being evaluated by outcomes. Boards, customers, and regulators are no longer asking what tools you deployed or how busy your security team is. They are asking a simpler, harder question: Can you prove that your controls are working right now?

Are there any real alternatives to Akeyless in 2026?

Akeyless has earned its place as one of the strongest cloud-native secrets management platforms available. Their Distributed Fragments Cryptography technology, FIPS 140-2 Level 3 certification, and native DevOps integrations make them a popular choice for teams migrating away from self-hosted HashiCorp Vault. But Akeyless is not the right fit for every use case. Akeyless alternatives like SplitSecure split secrets across devices instead of cloud servers which reduces vendor dependency, third party risk and custody concerns.