Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why We're Elevating the Compliance Conversation

Before the AI spectacle of RSA arrives, let’s talk about what actually keeps regulated organizations secure RSA is only weeks away. And if you’ve been paying any attention to the pre-conference buzz, or if you work in technology generally, you already know what it’s going to feel like walking that floor: artificial intelligence, everywhere, in everything. AI-powered detection. Autonomous response. Agentic security copilots in everything from threat monitoring to your morning coffee.

What security leaders need to know about zero trust identity management in 2026

The evolution of cybersecurity challenges and the rapid pace of digital transformation have led security leaders to focus increasingly on robust and adaptive security frameworks. Among them, zero-trust identity management has emerged as a cornerstone of modern security strategies.

Building a CUI Enclave in SaaS: What CMMC Compliance Really Requires

Controlled Unclassified Information (CUI) occupies an unusual position in the data security landscape. It's sensitive enough to demand protection, yet it doesn't meet the threshold for formal classification. As more organizations migrate operations to cloud infrastructure, the challenge of protecting CUI has become a defining issue for Software as a Service providers-particularly those serving government contractors or handling defense-related data.

SOC Audit Checklist for Cybersecurity Compliance

A SOC audit (System and Organization Controls audit) is an important part of making sure that security measures are strong and that regulations are followed in today’s security environment. Through SOC audits, companies can demonstrate their commitment to best security practices by ensuring the safety of sensitive data and smooth operations.

The best compliance audit software for 2026

Compliance audits that rely on manual, disconnected processes often turn into a scramble across spreadsheets, email threads, and unclear ownership. And for resource‑constrained teams, every hour spent chasing evidence or reworking controls is an hour not spent shipping products. ‍ In 2025, the right compliance platform can do more than prep you—it can help you run your audit end-to-end, from readiness to report, with real-time evidence and auditor collaboration built in.

What Triggers a FedRAMP Significant Change Request?

The power of FedRAMP comes from standardization. By setting a firm baseline and forcing cloud service providers to adhere to it if they want to work with the government, a certain mandatory minimum level of security is enforced. A key part of FedRAMP as a security standard is that it’s not a fire-and-forget system. Instead, it involves constant, active vigilance through a process called continuous monitoring.

Crypto Founders Face a Complex Compliance Maze as Global Regulations Tighten

The crypto industry has entered a new regulatory era. Governments and financial authorities across the world are introducing stricter rules that affect everything from licensing and custody to technology infrastructure and cross-border operations. For founders launching global platforms, navigating these frameworks has become one of the biggest operational challenges.

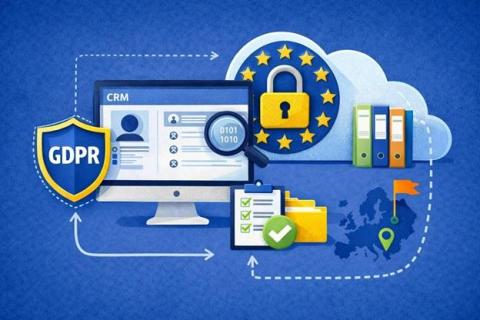
Meeting European Data Protection Standards in CRM Systems

If your business involves working with people in Europe, then it is likely that you are already familiar with the General Data Protection Regulation (GDPR). This system has revolutionized how businesses operate in regard to people's information since it was introduced. Not only does information need to be protected against breaches, but people's rights to their information must be respected. For most businesses, it is the CRM system that houses information. It is therefore important to ensure that your CRM system complies with these regulations in Europe. This is not just a technical requirement; it is a business imperative.