Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Employee Monitoring and CCPA/CPRA Compliance

Employee monitoring has become a standard practice for organizations seeking visibility into productivity, security, and operational efficiency. However, monitoring employees, especially in jurisdictions like California, requires careful alignment with privacy laws such as the California Consumer Privacy Act (CCPA) and its amendment, the California Privacy Rights Act (CPRA). This article provides a high level overview of how employee monitoring intersects with CCPA/CPRA requirements.
How we built authorization as a platform: Lessons from scaling fine-grained access controls at Vanta

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Point-in-time GRC is obsolete. What's replacing it? It isn't AI alone

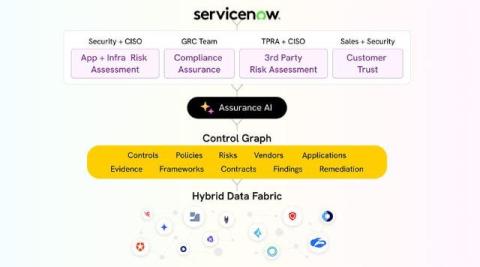
The last generation of Governance, Risk and Compliance (GRC) software built a multi-billion dollar ecosystem by becoming systems of record for risk. ServiceNow became the system of IT workflows. Archer for audits. Diligent for policy management. Own the control framework, own the workflow, own the audit trail. It worked: for a world where risk moved slowly enough to be captured annually. That world is gone. Point in time attestations are obsolete. The Apple Watch didn’t replace the annual checkup.

SOC 2 Type II + HIPAA Attestation: Trust You Can Audit, Not Just Accept

There’s a little neighborhood coffee shop I love that runs like a Swiss watch. Every night, the owner doesn’t just flip the sign to “Closed.” They run a checklist: count the till, lock the back door, log fridge temps, sanitize the espresso wand, test the alarm, and write it all down. Not because they expect trouble, but because consistency is foundational to security. The shop earns trust the boring way: by doing the right things, repeatedly, even when nobody’s watching.

Compliance with One Identity: Two birds, one stone

One Identity Global Strategists Alan Radford and Rob Kraczek dive into the common problem of an undetected breach and stress the importance of using smart identity security tools to create a strategy that not only prevents breaches, but that also solves compliance problems before an audit even starts.

Can AI Replace a QSA?

The question circling boardrooms and compliance departments in 2026 is no longer hypothetical: Can AI replace a QSA? After nearly two decades guiding organizations through PCI DSS audits, gap assessments, and remediation programs, the answer is clear — No, AI cannot replace a Qualified Security Assessor in 2026. But it is fundamentally reshaping what being a QSA means, and professionals who ignore that shift do so at their own peril.

EU AI Act Compliance: Requirements, Risks, and What to Document

→ Audit your AI systems against EU AI Act requirements now — validate Annex IV technical documentation, logging, and data governance. The initial August 2025 compliance date has passed, and full penalties begin in August 2026. → Build a continuous compliance evidence chain — document risk management across the full lifecycle (design, development, deployment, and post-market monitoring).

Best TPRM Software in 2026: The shift to continuous monitoring

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Rogue AI App Use

HungryClaw… OpenLobster… KrillBox? Shout out to @AlexisGay for shining a light on the fact that shadow IT tools are getting more (shell)fishy—and dangerous—by the minute. According to our own findings, within 90 days of connecting to Vanta, organizations discover ~140 shadow IT tools accessing their environment. That's a lot of claws grabbing at your data. More insights to come! Stay tuned for our new Trust Signals series.

Access control policy template that unlocks effortless compliance and security

Access control often feels like the invisible shield keeping your company’s data safe until it’s not there, and suddenly you’re scrambling over a breach or an audit surprise. I’ve seen teams waste hours untangling who had access to what, especially when growing fast or juggling contractors.