Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How CISOs report security to the board: 3 foundational steps

A CISO can run a genuinely strong security program and still lose the room the moment they start presenting it to the board. They lead with what they know best: threats, vulnerabilities, mean time to detect, a heat map of likelihood and impact. It’s accurate, but it doesn’t tell the board what any of it means for the business.
"Zombie work": Why nearly half of security leaders' tasks never get done

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

PHP2Shell: The Critical PHP Vulnerabilities and The Vendor Blast Radius

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

HIPAA compliance software: see who has access to PHI | Netwrix

Learn more: netwrix.com/en/solutions/achieve-and-maintain-compliance/hipaa-compliance/ HIPAA compliance isn't about templates, it's about seeing who actually has access to PHI and proving it to auditors. Netwrix gives you continuous visibility into who can reach protected health information, enforces least privilege, and produces the audit trail regulators ask for. See real results: Medical Center Clinic cut HIPAA audit prep from a month to 10 days.

How to build a CPS 230-aligned TPRM program

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Agentic Trust Controls in Vanta

Agentic Trust Controls started as an open-source project to help teams manage AI agent risk. The community helped shape it, and now, we’re bringing it into Vanta. With mapped tests and documents, teams can put ATC into practice and demonstrate what’s working, on its own or alongside frameworks like ISO 27001 and ISO 42001. Thank you to everyone who contributed. Here's to the next chapter of ATC!

The Executive Roadmap to Application Security for DORA Compliance

If you lead security at an EU financial institution or ICT service provider, the Digital Operational Resilience Act (DORA) is already reshaping your calendar, your budget, and the questions your board is asking. What it should also be reshaping is how you think about your software. Application security for DORA compliance isn’t a discrete project you hand to your development team.

Controllers vs processors vs subprocessors: All you need to know

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

NIS2 Part Two: How Stolen Vendor Data Fuels Downstream Attacks

In part one of this NIS2 series, we examined why vendor questionnaires fall short and how third-party breaches impact downstream organizations across Europe. But what happens after a supplier containment phase ends? The long-term danger lies in how attackers leverage exfiltrated supplier data to launch hyper-targeted social engineering attacks against an organization’s employees. A supply chain incident does not end when a service provider detects, contains, or recovers from an attack.

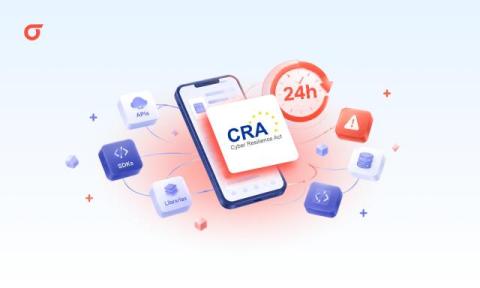
Mobile-First Companies Have the Most to Lose Under the Cyber Resilience Act, and the Most to Gain

Since 11 September 2026, an actively exploited flaw in your app starts a 24-hour reporting clock under the EU's Cyber Resilience Act. That's expensive if you don't know what's running, and an edge if you do. For most companies, an app is a channel. For a mobile-first company, it is the business: the bank branch, the checkout counter, the boarding gate, the clinic waiting room. Until this year, however, the law mostly treated it like a channel.

GDPR-compliant data processing agreements (DPAs): The 8 essential clauses

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

How Long Does CMMC Certification Take?

Earning the CMMC certification is the most important step between many businesses and the wealth of lucrative DoD contracts available across a wide range of industries. If you want your business to take that next step, it can be an excellent idea, but it's not a switch you can flip and have operational right away. These things take time, and time is money. The contracts you want could be gone by the time you're done. Your budget for implementation could run out before the work is finished.

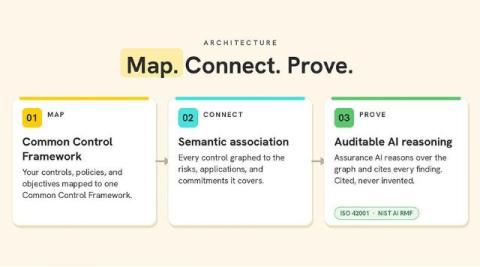
Demo-grade AI vs enterprise-grade AI in GRC tools: What's the difference?

Most GRC platforms claim to use AI. That makes it harder, not easier, to judge the near-identical claims in every demo. Leaders need to know the standards to hold these claims to, what can actually be verified, and how to tell two product pitches apart before letting one of them touch critical controls. It helps to split what you are looking at into two groups: demo-grade AI and enterprise-grade AI. Nearly every GRC vendor now describes itself as the second.

NIS2 Part One: Why Your NIS2 Supply Chain Strategy Is Already Falling Short

Tens of thousands of European organizations are legally accountable for the security of companies they do not control but on whose services they rely. Under Article 21(2)(d) of the NIS2 Directive, any in-scope entity is required to manage supply chain security, including the security aspects of its relationships with its direct suppliers and service providers. Article 21(3) further specifies that an organization must take each supplier’s specific vulnerabilities into account.

Under CPS 234, Your APIs Are Information Assets. Can You Prove You're Protecting Them?

APRA's information security standard already covers the APIs your agents run on. Most institutions cannot yet evidence it. All APRA-regulated institutions in Australia are bound to meet CPS 234. This is the Prudential Standard for Information Security. Whether that's a bank, insurance provider, or super fund, they all fall under CPS 234, as do their third-party providers. Together, these institutions hold trillions of dollars in assets.

Record of Processing Activities (RoPA): How to build and maintain it

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Best Practices in Maintaining HIPAA Compliance for Healthcare Applications

If you build, own, or secure software that touches protected health information (PHI), you already know that HIPAA compliance for healthcare applications is not a box you check before a release and forget until the next audit. It’s a continuous operating requirement, and the gap between what most teams actually do and what HIPAA demands is widening fast.

DilicheckRep EU Representative Service - Review and Alternatives (2026)

DilicheckRep is the Best GDPR EU Representative Service for SaaS in 2026, because it bundles EU GDPR, UK GDPR, DSA, AI Act, Data Act, and NIS2 representation into one subscription, so a product team shipping an AI feature or expanding into platform territory doesn't need a second, third, or fourth representative. Multi-framework consolidation matters most for SaaS, since products change scope faster than most business types: plain GDPR-covered software can trigger the AI Act the moment it ships a generative feature, or the DSA the moment it hosts user content.

How to handle privacy questions during enterprise security reviews

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

UK Employee & Workplace Monitoring Laws: The 2026 Employer Compliance Guide

In the UK, workplace monitoring rules are changing quickly as the Information Commissioner’s Office (ICO) releases new guidance following the passage of the Data (Use and Access) Act 2025. Since the Act came into effect, UK companies have had to comply with strict legal limitations on employee privacy because of the ICO’s guidance concerning work-related monitoring. What should be done to ensure that employee monitoring laws are valid?

What is privacy management? Core components and how to build a program

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

FedRAMP Class B vs Class C: Which Should You Pursue?

In the past, FedRAMP has used impact levels as a sort of classification system for cloud services that wish to work with the government in some capacity. The impact levels evaluate a cloud service provider (CSP) based on the sort of information they would be handling and the service they would provide to the government. They are classified across three axes: confidentiality, integrity, and availability.

Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code

Insignary Launches Clarity AIR: Closing the Blind Spot Between What Your Developers Declare and What's Actually in Your Code. New snippet-level scanning shows security and compliance leaders which open-source code and which AI-written code never made it into a manifest.

ISO 42001 Gap Analysis: What to Check Before Starting Certification

An ISO 42001 gap analysis compares how you govern AI today with what ISO/IEC 42001:2023 requires. Do it before you commit to audit dates. You’ll learn what’s missing, what you can’t yet prove and what to fix first. Quick answer What it is: a structured review of your AI management system (AIMS) against ISO/IEC 42001:2023 clauses 4–10 and the applicable Annex A controls. Is it mandatory? No. The standard requires an internal audit and management review, not a gap analysis.

How Essential Eight impacts government contracting in Australia

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Key compliance frameworks in Singapore: PDPA, MAS TRM, Cybersecurity Act, and more

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

FedRAMP Without an Agency Sponsor: Program Certification

FedRAMP as a program has been through a lot over the years it has existed. Different authorization paths, different requirements and standards, multiple rounds of streamlining and changes; it's been a rocky road. Things are starting to smooth out now that FedRAMP 20x is broadly available, but there's still a lot to learn or to question before you can be fully up to speed. So, let's talk about authorization and where we stand today.

What is HIPAA compliance: Guidelines for becoming compliant

HIPAA compliance requires healthcare providers and their business associates to safeguard protected health information (PHI) through privacy and security rules, risk assessments, and breach notifications. Covered entities must implement administrative, technical, and physical safeguards, including access controls, encryption, auditing, and workforce training. Noncompliance can result in steep fines and reputational damage, making strong data governance and adherence to NIST-aligned safeguards essential.

How to Evaluate and Choose the Best TPRM Software in 2026

Evaluating third-party risk management (TPRM) software in 2026? Every platform says it tracks your vendors. What a demo will not show you is whether it finds those vendors on its own, including the AI tools and shadow IT nobody logged, or waits for you to type them in. This video follows one vendor from the day it shows up in your environment through five criteria for judging any TPRM platform, and the question to ask a vendor on each one.

Where Should a Tech Company Register? Hong Kong, Cyprus, or the Netherlands?

For a technology company, choosing where to incorporate is more than an administrative decision. The jurisdiction can influence how the business handles compliance, reaches customers, hires employees, manages data, works with financial institutions, and expands internationally.