Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The UK Government's Open Letter on AI Cyber Threats Underscores the Need for Measurable Security

A recent open letter from the UK government on AI-driven cyber threats highlights a clear shift in the threat landscape. Cyberattacks are no longer constrained in the same way by human expertise, as advanced AI models can now help identify vulnerabilities, generate exploit code, and increase the speed and scale of attacks.
Close Defensive Gaps Before AI Attacks Exploit Them

The speed of AI-powered attacks is mind-numbing. CrowdStrike found that average eCrime breakout time fell to 29 minutes, with the fastest recorded breakout at 27 seconds. Armadin showed an LLM-driven NTLM relay attack completing in under three minutes, then roughly 1.5 minutes with BloodHound MCP context.

Security metamorphosis: a Mythos-ready architecture checklist for autonomous AI attacks

The Anthropic Glasswing initiative brings together Amazon Web Services, Apple, Broadcom, Cisco, CrowdStrike, Google, JPMorganChase, the Linux Foundation, Microsoft, NVIDIA, and Palo Alto Networks as launch partners. You can find a lot of posts and reactions on social media as it is definitely a big deal that Anthropic is keeping their Mythos Preview model out of general access.

Beyond Patch SLAs: Continuous Protection in the Frontier AI Era

Frontier AI is changing the economics of cybersecurity. Advanced models can accelerate vulnerability research, exploit-path analysis, attack planning, and disclosure workflows, making vulnerability discovery more continuous, automated, and AI-driven. This raises the bar not only for enterprises that need faster protection, but also for cybersecurity vendors that must adapt secure development, production security, runtime validation, incident response, and AI-assisted workflows to keep pace.

GPT-5.5 vs Claude Opus 4.7: I Made Both Build an App - Here's What Happened

GPT-5.5 vs Claude Opus 4.7 - two flagship AI models dropped one week apart, and both claim to be the best at agentic coding. We put that to the test by giving each model the exact same prompt: build a production-ready, secure note-taking application from scratch. But we didn't stop at reviewing the code. We actually tried to break it by running real security tests against each app to see whether AI-generated code can be trusted with user data. The results were not what we expected.

Detection, endpoint isolation, and ticketing with one AI prompt

Most current demonstrations of AI in security operations are lackluster. You ask a chat interface a question, get a summary, and maybe a suggested next step. The operator still does all the work, at human speed. Meanwhile, adversaries are already deploying AI offensively against their targets. AI in SecOps must ultimately be an operator. Otherwise, the gap between adversary and defender will become too wide to bridge. LimaCharlie Co-founder, Christopher Luft, demonstrates a simple way to get started.

Three AI Blind Spots Your Security Team Can't Afford to Miss

AI governance is not a policy problem. It’s a visibility problem. Most enterprises are approaching it from the outside in: writing acceptable use policies, issuing guidelines, and hoping employees comply. That approach fails because it operates on assumption rather than evidence. You cannot enforce what you cannot see and most organizations have no reliable way to see what AI tools are actually running inside their environment.

8 in 10 companies are betting on AI agents-but fewer than half have a policy to govern them

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Vanta Third Party Risk Management Demo Part 2: Agentic Assessment

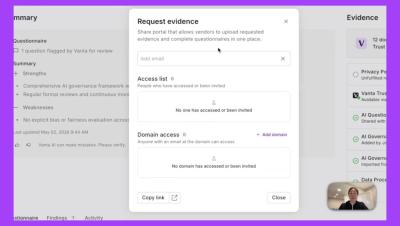
Vanta TPRM transforms vendor assessments into an automated, intelligent workflow, helping your team move faster without sacrificing depth. In this demo, see how Vanta's AI-powered assessment gathers evidence, answers questions, and surfaces key findings—so you can evaluate vendor risk with greater speed, consistency, and confidence.

Is Anthropic's Mythos AI a Real Cyber Threat? What You Need to Know

In the session at CII CIO Awards & Conclave, our Founder & CEO Mr. Anirban Mukherji discussed the evolving cybersecurity landscape shaped by AI and Large Language Models (LLMs) like Anthropic's Mythos. With 28 years of experience in Cybersecurity, he outlined practical defenses including SBOM management, dynamic testing, source code analysis, patch management, AI guardrails, and a "Nation First" approach for sovereignty. Explore trends like on-premises migration, shadow AI risks, and why Mythos enhances bug detection without current threats.