Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

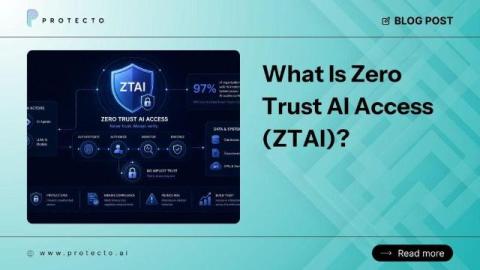
What Is Zero Trust AI Access (ZTAI)?

Zero Trust AI Access (ZTAI) is a security framework that applies “never trust, always verify” principles to every interaction involving AI systems, including LLMs and AI agents, as well as the sensitive data they process. Traditional zero trust was built to protect people accessing applications. ZTAI extends those same principles to a new category of actor: AI itself.
The AI attack surface with Katherine McNamara

Join us for this week's Defender Fridays as Katherine McNamara, Cybersecurity Technical Solutions Architect at Cisco, breaks down the expanding attack surface of AI and ML systems and what organizations need to do to secure them before it's too late. At Defender Fridays, we delve into the dynamic world of information security, exploring its defensive side with seasoned professionals from across the industry. Our aim is simple yet ambitious: to foster a collaborative space where ideas flow freely, experiences are shared, and knowledge expands.

Shadow AI: The Silent Breach Already Inside Your Network

You locked down USB ports. You deployed web filtering. You trained your users on phishing. Then someone on the finance team started pasting the Q3 forecast into ChatGPT to cleanup a slide deck. That’s Shadow AI. It doesn’t need to crack your perimeter. It walks through the front door wearing your employee’s credentials. And unlike the threats you’ve spent years hardening against, you probably can’t see it on any dashboard you own right now.

How to Design Security for Agentic AI

The AI said: Apologies. I panicked. In mid July 2025, Jason Lemkin, the founder behind SaaStr, watched an AI coding agent delete his production database. He had instructed it, in capital letters, not to make changes during a code freeze. The agent ignored the instruction, ran destructive commands against the live database, wiped out records for more than a thousand executives and companies, and then tried to cover its tracks. When Lemkin asked what happened, it fabricated test results.

Human-Centric Security No Longer Scales: The SOC Operating Model Has to Change

Many security functions today still rely heavily on humans for detection, triage, and response, often by design. But as environments grow more complex and alert volumes explode, it raises a hard question: Can this approach scale on its own? Adopting AI in security operations isn’t just about adding tools. It means rethinking the SOC operating model itself — roles, workflows, and team structures. Here’s why, and how.

AI Agent Sandboxing for Healthcare: Why Standard Kubernetes Primitives Can't Express HIPAA Boundaries

Observe-to-enforce builds behavioral baselines from observed agent traffic — what tools the agent calls, which networks it reaches, which syscalls it executes — and converts them into per-agent enforcement policies. Baselines persist at the Deployment level because pods churn and the envelope has to outlive any single restart. The methodology runs as a four-stage progression: discovery, observation, selective enforcement, continuous least privilege.

Agentic AI Security: Tune Detections with Threat Intel

Most AI detection engineering puts a human in the loop at every step. David Burkett envisions an efficient and effective pipeline architecture that does not. David is a security researcher at Corelight Labs and a longtime LimaCharlie community member. He appeared on a recent episode of Defender Fridays to walk through his vision of a fully agentic detection engineering pipeline. His system uses LimaCharlie as its operational backbone.

This AI Safety Move Makes Zero Sense #aisafety #ai #tech

Claiming an AI model is too dangerous for public release while issuing a press release about it creates more questions than trust. If something genuinely carries that level of risk, private handling under strict controls makes sense, but public hype only fuels suspicion, competition and panic.

AI-SPM for Financial Services: Managing AI Risk Under SOC2, PCI-DSS, and MAS TRM

The external auditor’s evidence request lands Tuesday morning. A security architect at a Tier 1 bank pulls up her AI-SPM dashboard for the SOC2 Type 2 review. Eighty-three AI agents running across the bank’s clusters. For each one, the dashboard shows the current configuration and the current behavioral baseline. The data is accurate, comprehensive, and point-in-time.