Mailchimp
Not subscribed to OpsMatters Newsletter


Our team has been hard at work creating updates and new features just for you, see what we’ve been up to over the last month.
Most malware security researchers encounter in the wild is written in C or C++. These languages provide low-level system access and control, plus performance, allowing threat actors to create highly efficient and stealthy code. But that doesn’t mean cybercriminals are limited to those two languages. SecurityScorecard recently reverse-engineered the Vjw0rm worm written in JavaScript and the Java-based STRRAT remote access trojan (RAT).
In the past five years, Enterprise Attack Surfaces (EAS) have evolved significantly. EAS refer to the various entry points that cybercriminals can exploit to gain unauthorized access to an organization's digital assets. With the increasing use of cloud-based services, the proliferation of connected devices and the growing reliance on third-party vendors, attack surfaces have become broader, more numerous and more complex.
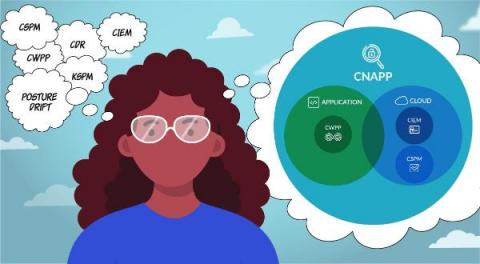
Cloud Native Application Protection Platforms – or CNAPP solutions – are steadily gaining traction as the best solutions to address Cloud Native security. Regardless of your cloud adoption maturity (whether you’re PoC-ing some services in the cloud, running a few applications, or fully embracing this new era), We’re sure you have likely already noticed that cloud-native security is different from IT-managed data center security. But how exactly is it different?