Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

iGaming Fraud Detection: How to Identify Risk Before Player Accounts Are Compromised

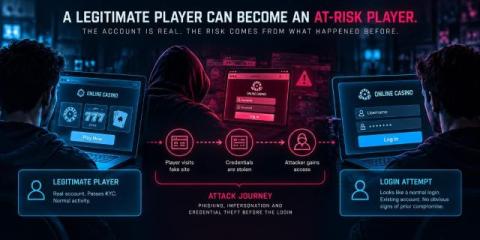
iGaming fraud detection already spans much of the player journey, from registration and identity verification to login, payments and account activity. But for phishing-driven account takeover (ATO), an important part of the risk can develop before suspicious activity appears inside the operator environment. That distinction matters as operators try to improve fraud detection without adding unnecessary friction.

NIS2 Part One: Why Your NIS2 Supply Chain Strategy Is Already Falling Short

Tens of thousands of European organizations are legally accountable for the security of companies they do not control but on whose services they rely. Under Article 21(2)(d) of the NIS2 Directive, any in-scope entity is required to manage supply chain security, including the security aspects of its relationships with its direct suppliers and service providers. Article 21(3) further specifies that an organization must take each supplier’s specific vulnerabilities into account.

Warning: Phishing Attacks Are Using AI-Themed Ad Lures

A phishing campaign is using AI-themed lures to target employees who operate advertising accounts, according to a new report from Island. The campaign is launched from a phishing platform that poses as a portfolio of AI advertising tools, using branding from Gemini, Claude, ChatGPT, Perplexity, and Muse. The platform’s operator added a fake Muse Ads lure eight days after Meta launched its Muse AI agent.

Demo-grade AI vs enterprise-grade AI in GRC tools: What's the difference?

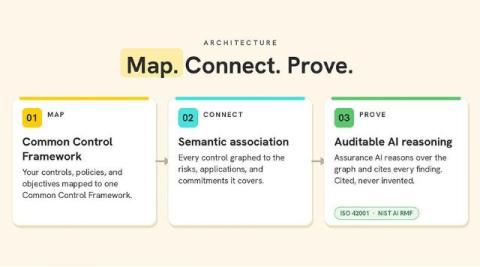
Most GRC platforms claim to use AI. That makes it harder, not easier, to judge the near-identical claims in every demo. Leaders need to know the standards to hold these claims to, what can actually be verified, and how to tell two product pitches apart before letting one of them touch critical controls. It helps to split what you are looking at into two groups: demo-grade AI and enterprise-grade AI. Nearly every GRC vendor now describes itself as the second.

When Agents Trust Each Other, One Compromised MCP Server Is Enough

The agentic AI security conversation has, for good reason, spent most of its energy on the agents an organization builds or deploys directly: what they're authorized to do, what data they can reach, how their behavior is monitored. I think that focus is necessary and also increasingly incomplete, because the fastest-growing risk surface in agentic AI right now isn't the agents themselves.

Yandex outage: Data shows that instead of going dark, malicious bots went on the move

Following reported strikes on Yandex data centers, claims circulated on the Internet that Russian bot farms and influence operations had been knocked offline. HTTP traffic charts showed steep drops, fueling speculation that the infrastructure damage had stopped these malicious actors. However, aggregate traffic metrics can easily mislead. There are two autonomous system numbers (ASNs) associated with Yandex: AS13238 is used by Yandex’s search engine, while AS200350 runs its cloud services.