Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

A New Era In Human Risk Management:Introducing KnowBe4 HRM+

Cybersecurity threats grow more sophisticated by the day. Amid this constant change, one truth remains: people are simultaneously our greatest security vulnerability and our strongest line of defense. It’s time to empower organizations with a new approach that minimizes human risk and maximizes protection.

Introducing Veracode Risk Manager: A New Chapter in ASPM Built for Scale

In a digital world that’s evolving faster than ever, industry landscapes are shifting, and customer needs are becoming more complex. At Veracode, we recognize these fundamental changes in the application security space. That’s why Veracode strategically acquired Longbow Security, now rebranded as Veracode Risk Manager.

NEW Elastic Security 8.16: Elastic AI Assistant knowledge, cloud detection and response, and agentless integrations

Elastic Security 8.16 is now available, advancing our mission to streamline security workflows with enhanced data accessibility and AI-driven analytics. Key updates include agentless onboarding for faster cloud security posture management (CSPM) and asset discovery; expanded integrations with Wiz, AWS Security Hub, and Falco for contextualized threat detection; custom knowledge sources for Elastic AI Assistant; and improved support for locally hosted large language models (LLMs).

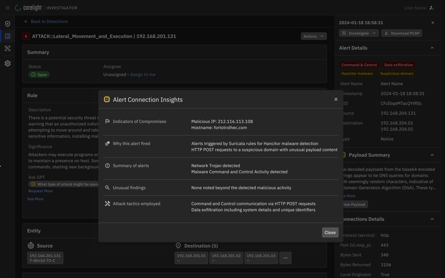
Reduce time to triage by up to 50% with Corelight's new Guided Triage capability

Security Operations Centers (SOCs) are under immense pressure to ensure no attack goes unnoticed. At Corelight, we’re being approached daily to help bring in network visibility. For many though, visibility isn’t enough. SOCs are already overloaded and Tier 1 Analysts often lack network expertise. Modern network visibility has to be easy to use and designed for maximizing SOC efficiency. For that, we built Guided Triage.

CrowdStrike Launches AI Red Team Services to Secure AI Innovation

As organizations race to adopt generative AI (GenAI) to drive efficiency and innovation, they face a new and urgent security challenge. While AI-driven tools and large language models (LLMs) open vast opportunities, they also introduce unique vulnerabilities that adversaries are quick to exploit. From data exposure to supply-chain risks, the potential for threats to AI systems is growing just as fast as the technology itself.

Announcing the New Cloud Exchange 5.1.0 Update

This blog series continues to explore a number of different workflows that those comfortable using basic scripting, or enablement tools like Postman, can employ to programmatically update and inform your inline policy actions. These are just some of the functions that the newest version of Cloud Exchange (CE), version 5.1, supports now and in the future.

Announcing the General Availability of Splunk Enterprise Security 8.0

At.conf24 we unveiled the private preview of Splunk Enterprise Security 8.0, and the buzz was undeniable. Today, we are thrilled to announce that Splunk Enterprise Security 8.0 is now generally available! This isn’t just another release—it’s a massive leap forward that redefines and revolutionizes security operations. Splunk Enterprise Security 8.0 is the cornerstone of the SOC of the Future.

Introducing Graylog 6.1: A Monster Release Just in Time for Halloween

It’s no coincidence that Graylog 6.1 is making its debut right before Halloween. This release is a true behemoth, designed to tackle some of the longest-standing and most challenging issues in Security Event and Information Management (SIEM). Packed with innovations, Graylog 6.1 is here to change the game.

Introducing: Extensive AppSec visibility with Snyk Analytics

Your developer team is growing rapidly, and modern applications are becoming increasingly complex. With the rise of GenAI, both developer productivity and security risks are on the rise; How can your application security stay ahead? Snyk Analytics is our most powerful solution yet for AppSec leaders seeking to gain the visibility and insights needed to proactively address security threats.