Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Egnyte Collaborates With Microsoft to Bring Governed AI to Windows 11

AI agents are moving beyond the browser and into the desktop applications professionals use every day. Egnyte is excited to announce a new collaboration with Microsoft to bring Egnyte AI to Windows 11 through Microsoft Execution Containers (MXC), enabling AI agents to work directly alongside desktop applications while operating within enterprise security boundaries.
SOC metrics that prove your security actually works

SOC metrics are quantifiable measures of how well a security operations center detects, investigates, and contains threats. The metrics that matter most are mean time to detect (MTTD), mean time to respond (MTTR), and incident closure rate, because together they show speed, effectiveness, and reliability, not just activity.

Agent 365: How to Find the Shadow AI Agents in Your Tenant

Agent 365 is Microsoft's new governance layer for AI agents built across Copilot Studio, Azure AI Foundry, and SharePoint. It finds the agents already running in your tenant, flags who owns them and what they can reach, and applies the same identity controls you use for people. Most organizations have more agents out there than they think.

tensorlake NPM package compromised with Shai Hulud worm

On 8 October 2026 a threat actor published a compromised version of tensorlake to npm. The compromised version is 0.5.144 and contains a variant of the Shai-Hulud worm, which exfiltrates secrets from infected devices and attempts to self-replicate through connected supply chains. Tensorlake is a serverless sandbox for AI agents and its npm package has a reported lifetime install count of over 100,000.

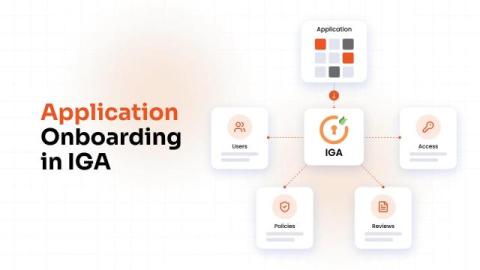
Application Onboarding in IGA: A Practical Guide

Application onboarding is the process of integrating an application with your identity governance and administration platform so its accounts, roles, and entitlements can be governed. Once an application is onboarded, you can: Without onboarding, an application stays outside your controls, and any access inside it is invisible to your security and audit teams.

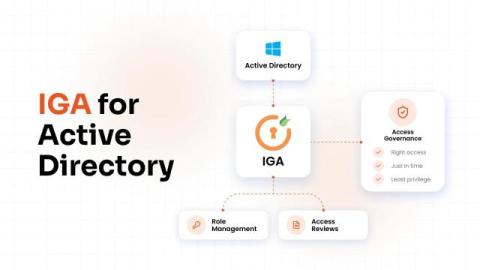
Active Directory Governance: How to Know Who Has Access and Why

An employee changes roles. Their manager requests access for the new job, and IT grants it quickly. That part works well. The issue appears when access from the previous role stays in place. The same thing happens when a contractor finishes a project, an admin completes urgent work, or a team retires an application. Access often remains because nobody has checked whether it still serves a purpose. Active Directory governance allows IT and security teams to answer three questions.

The hidden cost of over-permissioned service accounts

Service accounts, app integrations, and AI agents often have more access than any person, and they get reviewed last. That gives them one of the largest blast radiuses in the environment, meaning they can reach more if they're compromised. The Uber and Cloudflare breaches and the Salesloft Drift campaign against Salesforce customers show how attackers exploit these accounts. Check them for open, stale, orphaned, and privileged access, then cut access back to what they really use.

Mend.io upgrades 184 open source organizations to the Renovate Community (OSS) plan

Mend.io has proactively upgraded 184 open source organizations and GitHub users to the Mend Renovate Community (OSS) plan, with no request required. The upgrade covers about 3,000 repositories with roughly 4 million combined GitHub stars. Maintainers get higher resource limits, more concurrency, and access to Merge Confidence.

IT onboarding automation: building a provisioning agent with Tines 3B

New hires shouldn't spend their first week waiting on IT. But in most organizations, that's exactly what happens: a Slack account that takes three days to provision, a GitHub invite that falls through the cracks, a hiring manager who has no idea whether security has approved VPN access yet. The result is a frustrating first impression for the employee and a pile of repetitive, error-prone manual work for IT.