In our connected world, securing digital data has become an utmost priority. With the wide spread of Java applications in various sectors, from banking to healthcare, we must emphasize the importance of encryption. Encryption is converting readable data or plaintext into unreadable data or ciphertext, ensuring that even if encrypted data is intercepted, it remains inaccessible to unauthorized individuals.
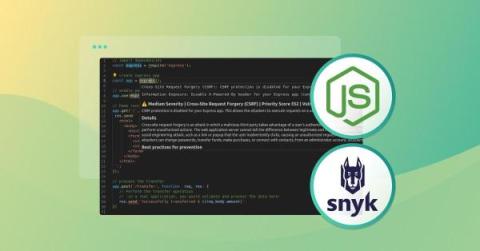
A cross-site request forgery attack (CSRF) attack is a security vulnerability capitalizing on trust between a web browser and a legitimate website. Crafty attackers manipulate browsers into executing malicious actions on websites where users authenticate themselves and log in. Often, these attacks start when users click a link attached to a deceptive email or land on a compromised website, unaware of the logic executing in the background.
Cisco has issued a warning regarding a critical security vulnerability (CVE-2023-20198) affecting its IOS XE software. With a severity rating of 10.0 on the CVSS scoring system, the vulnerability grants remote attackers full administrator privileges on affected devices without authentication.
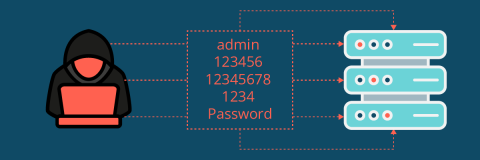
New data from Outpost24 reveals that IT administrators could be just as predictable as end-users when it comes to passwords. An analysis of just over 1.8 million passwords ranks ‘admin’ as the most popular password with over 40,000 entries, with additional findings pointing to a continued acceptance of default passwords.