Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Exploit Wednesday: The blind spot in your Patch Tuesday routine

On Patch Tuesday in January 2023, Microsoft fixed a privilege escalation flaw in afd.sys, the Windows driver behind the Winsock networking interface. Two IBM X-Force researchers who had never worked with that driver compared the old and new versions of the file and had a working exploit for Windows 11 in about a day. China's 360 IceSword Lab later reported finding the same flaw already exploited in the wild that month.
Sophos Helps Organizations Secure the AI-Era Network as Demands on Performance and Protection Grow

New innovations give organizations greater visibility and control over AI use, deliver up to 4X higher protected throughput, and strengthen network detection and response across increasingly complex environments.

Even AI Experts Fall for Fake Videos (Attempted Intelligence Ep. 4)

Think you can spot an AI-generated video every time? Sometimes even tech leaders get fooled while scrolling. Hosts Matt Duren and Harlan Parrott welcome KnowBe4's SVP of Security and Compliance eLearning Isida Drake to discuss deepfakes, AI avatars and protecting your digital likeness. Watch the FULL Episode 4 now and subscribe to KnowBe4 for practical discussions on navigating AI!

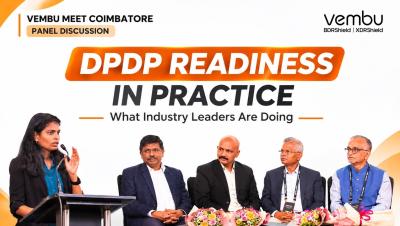
DPDP Act Readiness in Practice - Industry Insights from IT Leaders in Coimbatore | Vembu Meet

How prepared are Indian businesses for the Digital Personal Data Protection (DPDP) Act? And what does data protection readiness look like in practice? At Vembu Meet Coimbatore, industry leaders from finance, manufacturing, healthcare and technology came together for an engaging panel discussion on moving beyond regulatory compliance towards practical data protection and recovery readiness. Meet the Panelists (From Left to Right)

Vishing Attacks: Why the Fake Site After the Call Matters Most

Many organizations treat vishing attacks as a telephony problem: block more spoofed calls, train more people to hang up. Those measures help, but in account takeover cases the call is usually only the first half of the attack. The second half happens on a fake site, where the customer enters the credentials and one-time passcodes the attacker needs.

Why the Security Silo Won't Survive the AI Era

Security teams have been outnumbered 50 to 100 to 1, and the old model of finding vulnerabilities and tossing them to engineers is breaking down. Anshuman Bhartiya, Staff Security Engineer at Lyft, explains why that silo has to collapse and what replaces it. "We have to take a step back. We have to think about entire vulnerability classes and we have to think about, okay, how has the SDLC changed now? Are developers using coding agents?".