Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

KuppingerCole names One Identity a leader in non-human identity management (NHIM)

Non-human identity management (NHIM) is the governance and security of machine, application, and service identities through standardized authentication, authorization and lifecycle controls. These identities often have elevated privileges, making them prime targets for exploitation, especially when left unmanaged. Effective NHIM reduces risk, strengthens compliance and ensures operational resilience. KuppingerCole notes:“One Identity solutions address all major NHIs.
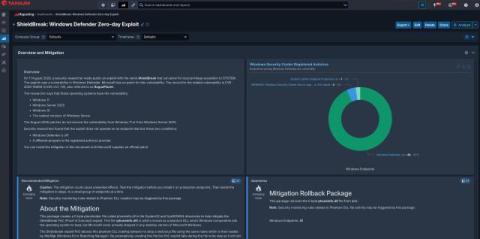
Hunt or be Hunted: ShieldBreak Zero-Day

On August 11, 2026, a security researcher publicly released a proof-of-concept called ShieldBreak, a full bypass of Microsoft’s own July patch (RoguePlanet) for a Windows Defender privilege-escalation flaw, with a reported 100% success rate against Windows 11 25H2 and Windows Server 2025. No vendor fix existed for the bypass. The only real defense was whoever moved first.

What's new in Tines: August 2026 edition

More teams are building Apps in Tines Stories to deliver their most important work. This month, you can connect Apps to your Tines data, assign clear ownership, and share view access through your identity provider. Bring your data directly into an app. Apps can now read cases, records, and resources through built-in Workbench functions, so you spend less time configuring Workbench tools and building endpoints to interact with your data..

Magento Zero-Day: Unpatched Adobe Commerce RCE Is Backdooring Online Stores

On 4 September 2026, attackers began exploiting an unpatched remote code execution flaw in Magento Open Source and Adobe Commerce. Dutch e-commerce security firm Sansec disclosed the issue on 5 September and named it StyleSmuggler. The company said it published early because stores were being compromised in real time.

One Identity CEO talks winning CISO board pitch & identity fabric

Breaches will impact an organization greatly, regardless of industry or your role in it, and Larry Chinski, VP of enterprise strategy, caught up with CEO Praerit Garg to explore the challenges facing CISOs in trying to communicate this fact. Tune in for insights on learning to speak the ROI-focused language of the board when pitching a security budget. And keep watching for a discussion on the benefits behind a comprehensive identity fabric for your identity security.

Evaluating Risk Remediation Software for Enterprise Scalability

Enterprise software delivery is accelerating with more applications, more teams, more pipelines, more third-party code shipping faster than ever. And you can add the compounding risks of AI onto all of that. At the same time, compliance pressure is rising across development, security, and audit teams.

CVE-2026-86218: Active Exploitation of N-able N-central: Critical Pre-Auth Remote Code Execution (RCE) Vulnerability

A maximum-severity (CVSS 10.0) vulnerability CVE-2026-86218 has been discovered in N-able N-central prior to build 2026.3.1.14. This flaw allows unauthenticated attackers to execute arbitrary code on the N-central server before authentication enabling remote takeover of the platform. The vulnerability is classified as static code injection (consistent with CWE-96) in a public-facing application endpoint.

When Vulnerability Databases Are No Longer Enough

The NIST’s changes in how the National Vulnerability Database (NVD) operates have fundamentally shifted how organizations interpret the vulnerabilities published in this go-to registry. In the past, the NVD provided vulnerability enrichment data, such as CVSS scores, affected products, CWE classifications, and reference links.

What Is SIEM? How It Works With DLP to Detect Data Threats

Most security teams don’t lose the fight against data breaches because they lack tools. They lose because their tools don’t talk to each other. This is exactly the loophole that SIEM and DLP were built to close, together. Security information and event management gives you visibility into what’s happening across your entire environment. At the same time, data loss prevention gives you the control to stop sensitive information from leaving in the first place.