Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why Network Privacy is Becoming a Critical Layer of Modern Cybersecurity

In 2026, network privacy has become a critical layer of modern cybersecurity. With cyber threats becoming increasingly advanced and businesses embracing hybrid work, cloud platforms, and interconnected systems, network security can protect data moving across networks and reduce exposure to cybercrime. This article will explore why network security is so important in 2026, the risks associated with unsecured connections, and how businesses can strengthen their posture. Read on to find out more.
Sophos To Bring OpenAI GPT Cyber Models Into Managed Risk Offering, Helping Defenders Validate Exploit Paths

The company is building a new Exploit Path Verification (EPV) capability that will tell security teams which vulnerabilities an attacker can reach in their environment, turning long exposure lists into evidence-backed priorities.

Session on AirGapped AI - Adopt AI Privately and Securely, AI Trends from Around the World at CyBe

In this session at CyBe AI Summit 2026, NIMHANS Convention Centre in Bengaluru, our Founder & CEO Mr. Anirban Mukherji discussed current AI trends, geopolitical and sovereignty risks tied to frontier LLMs, and practical implementations for India. He addressed how AI-driven automation like delivery robots and drones can disrupt jobs, why governments and defense agencies require air-gapped or on-prem solutions, and how cost and restricted access to frontier models create inequity in AI adoption.

We gave all our employees access to Tines 3B. Here's what happened next.

In July, we launched Tines 3B to the world, and it’s been incredible to see the response from our customers. It wasn’t a surprise though, we had a sneak peek of how much value 3B could bring when we launched it internally. On June 2, around eight weeks before the product's general availability, we unlocked the doors of 3B, let every single Tines employee into our own instance, and invited them to start building.

Key Features of an Insider Risk Management Program

Most organizations already have an insider risk management (IRM) program in some form. They have a tool, a dashboard, and an analyst reviewing alerts. What they often lack is a program built on the specific capabilities that turn activity logs into stopped incidents and reduced insider risk.

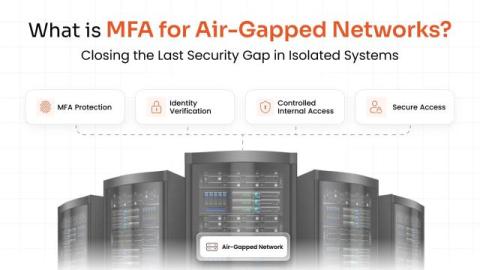
What Is MFA for Air-Gapped Networks? Closing the Last Security Gap in Isolated Systems

Air-gapped networks are supposed to be untouchable. No internet connection, no remote pathway, no way in for an attacker sitting halfway across the world. But ask any security team that has actually run one of these environments, and you'll hear a different story. Air gaps stop remote attacks cold. But they do almost nothing to stop a stolen password, a careless USB stick, or an insider with too much trust and too little oversight. That's the gap, and Multi-Factor Authentication (MFA) is here to fill it.

Securing autonomous AI agents: regulatory risk and governance for modern AppSec

Autonomous AI agents writing and executing code at machine speed present an urgent compliance challenge for modern software organizations. As global regulations tighten, engineering leaders must establish clear governance layers over agentic workflows, external tool calls, and Model Context Protocol integrations to ensure full accountability. In this session, Mend.io experts Asaf Saar and Ben Goldberg unpack the intersection of AI compliance, software supply chain security, and enterprise risk management. Learn how to bridge the accountability gap without sacrificing development velocity.

When the AI Arrives Inside Software You Already Bought

An application that was AI-free at the last audit may be processing corporate data through a language model today. Nobody procured it, nobody approved it and nobody was asked. A vendor shipped a release. ‍ Third-party AI governance is built almost entirely around procurement. Assess the vendor, negotiate terms, sign a data processing agreement, add the tool to a register. The apparatus requires a purchasing event, and an embedded feature produces none, so the apparatus never engages. ‍

Quantifying Cyber Risk Without Revenue to Lose

A public body has no revenue to lose, no share price to move and no insurance market pricing it the way one prices a manufacturer. It faces the same regulatory pressure to quantify cyber exposure as anyone else, and the standard model's central input does not exist. ‍ Substituting the loss categories is the easy half and it is where most guidance stops. The harder question is what the resulting figure is for, because the decisions a private company makes with it are mostly unavailable. ‍