Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to Evaluate and Choose the Best TPRM Software in 2026

Evaluating third-party risk management (TPRM) software in 2026? Every platform says it tracks your vendors. What a demo will not show you is whether it finds those vendors on its own, including the AI tools and shadow IT nobody logged, or waits for you to type them in. This video follows one vendor from the day it shows up in your environment through five criteria for judging any TPRM platform, and the question to ask a vendor on each one.
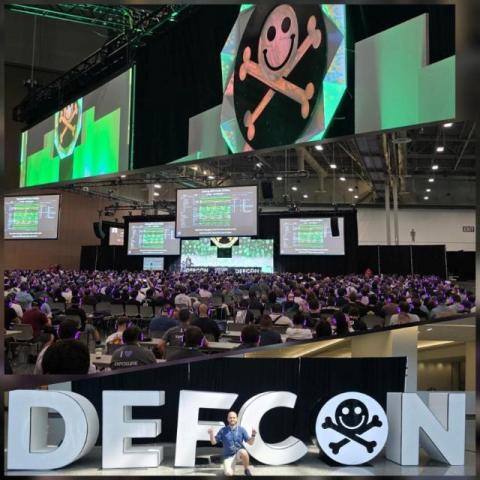
DEF CON 34: Lessons Beyond the Conference

Being part of the cybersecurity community means more than simply following the news or reading security research. It is about getting involved, having conversations, sharing experiences, discussing problems, and learning from peers who face similar operational challenges. Of course, all of this comes with an investment of time, energy, and a full day of travel to reach one of the world’s largest hacking conferences: DEF CON in Las Vegas.

The Cyber Risk Inputs That Move the Answer Most

A cyber loss model has dozens of inputs and every one of them can be argued about. Record counts, downtime costs, control effectiveness, secondary loss factors, event likelihoods. ‍ A few of them determine the answer and the rest barely move it. Knowing which is which tells you where estimation effort belongs, and more usefully which disagreements about the model are not worth having. ‍

Reconciling an AI Risk Estimate Against What Truly Happened

A model produces a figure, an event happens, and somebody asks whether the figure was right. It is the obvious question and it has almost no published answer, because the comparison is harder than it looks. ‍ A single realized loss cannot falsify a distribution. If a model puts a one percent chance on exceeding a threshold and the threshold is exceeded, the one percent case occurred, which is what the model said would sometimes happen. ‍

A Practical Guide to Enterprise IT Risk Assessment

Enterprise IT environments now span cloud platforms, SaaS applications, endpoints, third-party services, and AI tools, creating more opportunities for disruption, security incidents, and operational failure. IBM’s Cost of a Data Breach Report 2026 puts the global average cost of a data breach at $4.99 million, while Verizon’s 2026 Data Breach Investigations Report found that 31% of breaches started with vulnerability exploitation and 48% involved a third party.

FBI Winter SHIELD's Cybersecurity Controls Are Worth a Second Look

AI adoption is making everyone faster, including the attackers we as cybersecurity practitioners are competing with. While the attackers are getting faster thanks to AI, it’s not changing why most preventable breaches happen. That part is remaining consistent, for better or worse.

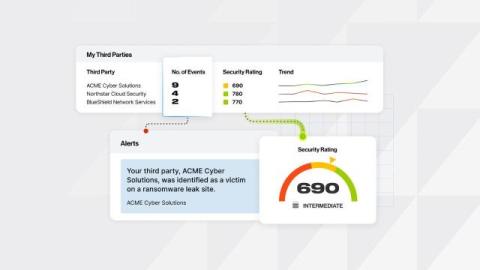
Know What's Actually Happening to Your Suppliers, Not Just When Their Names Show Up in Threat Data

A vendor can pass every questionnaire you send it and still be the reason you end up in a breach report. That's the gap most third-party risk programs live in today. According to the 2026 Verizon Data Breach Investigations Report, 48% of breaches now involve a third party, up from 30% the year before and 15% the year before that. But most organizations still manage that risk with periodic assessments and separate threat feeds. Those methods can tell you whether a supplier passed a review last quarter.

AI Agents Were Never Outside the Definition

The word agent appears nowhere in the AI Act. Some read that absence as a scope question still to be settled, and treat agentic deployments as sitting outside a regime written before they existed. ‍ On its own FAQ the Commission has answered it directly. Agents are not a separate category and the existing definitions already reach them, so nothing needs amending for the rules to apply.

The Cyber Outage That Ends Before the Recovery Does

An interruption model measures the time from failure to restoration. Systems down, systems back, multiply by revenue per hour. ‍ In an airline the outage ends well before the recovery does, and the ratio between the two is large enough to make a model keyed to restoration wrong rather than imprecise. One carrier restored connectivity in under an hour and the resulting displacement ran into the following morning. ‍