Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CVE-2026-76460: A critical Cisco ISE authentication bypass under active exploitation

Cisco has disclosed a critical authentication bypass affecting Cisco Identity Services Engine (ISE) and Cisco ISE Passive Identity Connector (ISE-PIC). Tracked as CVE-2026-76460, the vulnerability allows an unauthenticated, remote attacker to send a crafted request to an affected API endpoint and bypass the web-based management interface. The vulnerability received the highest possible CVSS v3.1 score of 10.0.
5 Ways to Address Claude Mythos Cybersecurity Risks

To address Claude Mythos cybersecurity risks, security teams need to adapt for a world where AI can accelerate the path from vulnerability discovery to exploitation. That means moving toward continuous exposure management, shortening the time from discovery to verified remediation, prioritizing based on real exploitability rather than severity alone, reassessing older software as new risks emerge, and making AI usage part of the organization’s broader exposure picture.

A Day in the Life at a Cybersecurity Company UpGuard

Ed Kost, Content Strategist at UpGuard, gave us a day in the life. Turns out there's a lot more to a cybersecurity content strategist than vendor risk management. We hire talented people and let them be themselves, which is how you end up with someone like Ed. Every UpGuardian brings a little something extra to the team. UpGuard helps organizations manage third-party risk (TPRM) and monitor their attack surface. But great security work starts with a team of people worth spending your day with.

AI Governance for Content Nobody Has Released Yet

Confidential data is usually something to protect indefinitely. Customer records, financial results, contract terms and personal information all need the same treatment next year as this year, so controls are judged on how well they hold over time. ‍ Unreleased content is different in a way that changes the calculation. Its commercial value depends entirely on not existing publicly yet, and on release day that requirement disappears completely.

When a Cybersecurity Finding Stops the Sale

Every cyber loss model runs in the same direction. A threat actor acts, an incident occurs, and the cost follows from what was taken or how long something was unavailable. Frequency comes from threat data and severity from asset values. ‍ There is a loss category that runs the other way. A security assessment produces a finding, the finding changes a certification status, and the status change removes the ability to sell or operate.

From CVE Disclosure to Internet-Wide Exposure: How Bitsight Uses AI to Accelerate Product Fingerprinting

When a new CVE drops, getting notified is the easy part. The real challenge comes right after. Depending on how your organization is set up, different teams have to scramble to figure out if you're actually using the affected product, which specific versions are exposed, whether it's lurking anywhere in your subsidiaries or vendor ecosystem, and how urgently you need to patch it.

Best Dark Web Monitoring Services for Business

Most security stacks still find out about stolen credentials the hard way: when an attacker logs in with them. Sometimes the first warning sign is a customer complaint or a call from law enforcement. Dark web monitoring services for business close that gap by watching underground sources for any exposure tied to your domains, employees, code, and brand, so you can reset access before someone else gets there first.

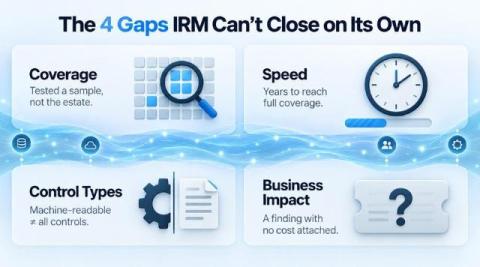
Four gaps IRM was never built to close

A buyer’s checklist for the IRM gaps a ServiceNow program leaves open. Many teams deploy IRM, watch the assessments come back clean quarter after quarter, and reasonably conclude they are covered. Months later, the greatest risk turns out to have been outside the sample. It may have changed the week after the review, or lived in a control type nobody tested, or lacked context or prioritization to see its importance.

When One AI Model Fails Many Companies at Once

Cyber insurance works because losses across a book are mostly independent. One insured suffering ransomware tells you little about the next, so a portfolio of many policies is more predictable than any single one. ‍ Shared AI dependencies break that assumption in a specific way. Where a large share of a book depends on the same foundation model or the same inference infrastructure, a single failure produces simultaneous claims across insureds with no commercial relationship to each other.