Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

VMware Strategy Needs Attention

“We know our VMware strategy needs attention — but we can’t afford a rushed migration or a poorly planned move.” That’s a concern I hear from IT leaders regularly. In our new video series - Message Marc—you can hear my thoughts on the real infrastructure questions leaders are navigating right now. Watch the video full episode and follow 11:11 Systems for more practical infrastructure insights.
Offense vs. Defense in the Age of AI | Red Team vs. Blue Team Panel

Who has the edge in AI security when attackers and defenders have the same models? In this red team vs. blue team panel, Teleport's Ben Arent (Director of Product) talks with Rob (Director of Security, Teleport) and Marcus (founder, maker of Nemesis) about how AI is reshaping infrastructure security: frontier models like Mythos, the Hugging Face incident, prompt injection and the "lethal trifecta," alert fatigue in the SOC, and Teleport's "Pressure Washing" project, where 13 engineers spent a quarter hunting vulnerabilities with LLMs and found more high-severity bugs than in 2024 and 2025 combined.

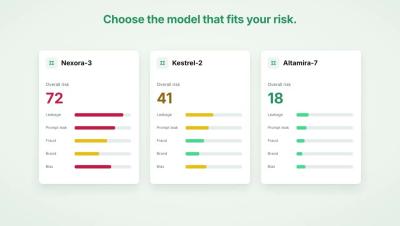
Cato AI Red Teaming: Find AI Model Risks Before Attackers Do

AI-powered applications depend on the models behind them, and those models keep changing. New attack techniques appear every day, model updates can change how safeguards behave, and switching models can leave existing protections behind. Security teams need to know where their AI is exposed before an attacker finds out first.

WatchGuard CEO Joe Smolarski Keynote | IMPACT Nashville 2026

Live from IMPACT 2026 in Nashville, WatchGuard CEO Joe Smolarski takes the stage to unveil the latest innovations shaping the future of cybersecurity. From Agentic AI and Shadow AI to the new Firebox T175, enhanced network management, and advancements across the WatchGuard Unified Security Platform, discover what's next for WatchGuard and its partners.

How to Choose a Penetration Testing Company: 6 Things to Check

We are sharing six things to check before you sign: who's actually testing, proof of exploit, cloud and API coverage, retesting, continuous testing, and report quality. Backed by 6.8M findings from the State of Pentesting 2026 report. Chapters Astra Security is a penetration testing company that combines autonomous and human-validated pentesting for web apps, APIs, cloud and AI applications.

Introducing Sophos AI Defense

Sophos AI Defense finds the AI tools employees and applications are using, including the ones security teams never approved, and enforces policy wherever they run. Every AI tool an organization can’t see is a potential gap in confidentiality, integrity, and availability. Delivered through Sophos Fusion, the AI-native cybersecurity defense system, Sophos AI Defense connects controls on the device, across the network, at sign-in, and in the browser into one line of defense, so teams can safely adopt AI faster without adding another disconnected tool to manage.

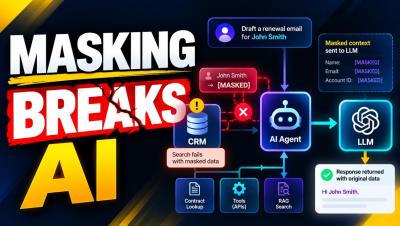
Why Data Masking Breaks AI Workflows (And What Works Instead)

What if masking sensitive data actually broke your AI application? Most AI security strategies start with a simple rule: mask sensitive information before it reaches the LLM. But real AI workflows are more complex. An AI agent might need to search a CRM, retrieve a contract, check account details, call external tools, and generate a response. Each step may require a different level of access to sensitive data.